Repository navigation
feat: validate aggregate IAM policy and template limits - #1030
Merged
Merged
Conversation


alongubkin
added this pull request to stack #1031
October 14, 2026 08:50

|
Enclave skipped this draft pull request. It will run automatically when you mark the PR as Ready for review. |
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 08:56
7b146ee to
b3cc7fa
Compare
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 09:17
b3cc7fa to
77475ec
Compare
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 09:22
77475ec to
3977186
Compare
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 09:38
3977186 to
3e26f8b
Compare

Member
Author
|
@greptileai review |

 [High impact] This PR appears safe to merge after its base PR. SummaryThis PR adds early AWS IAM quota checks and checks the final CloudFormation and Terraform output.
Diagram%%{init: {'theme': 'neutral'}}%%
flowchart TD
A[Stack configuration] --> B[Build-time IAM check]
B --> C[Prepared stack and deployment values]
C --> D[Direct setup aggregate check]
D --> E[Runtime policy checks]
E --> F[AWS writes]
C --> G[CloudFormation or Terraform generation]
G --> H[Final role quota check]
H --> I[Template output]
Reviews (6) · Last reviewed commit: "feat: validate aggregate IAM and templat..." · Reviewed by Greptile |


alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 11:36
3e26f8b to
8ae4128
Compare
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 11:51
8ae4128 to
f785497
Compare
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 15:14
f785497 to
6694d8b
Compare
alongubkin
removed this pull request from stack #1031
October 14, 2026 15:15
alongubkin
added this pull request to stack #1033
October 14, 2026 15:15
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 15:34
6694d8b to
53a30e0
Compare
Member
Author
|
@greptileai review |
alongubkin
marked this pull request as ready for review
October 14, 2026 15:51
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 16:14
53a30e0 to
5d0331c
Compare
alongubkin
marked this pull request as draft
October 14, 2026 16:15
This was referenced Oct 14, 2026
alongubkin
marked this pull request as ready for review
October 14, 2026 16:26
alongubkin
marked this pull request as draft
October 14, 2026 17:15


Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
alongubkin
force-pushed
the
alon/alien-5-quota-5-iam
branch
from
October 14, 2026 17:17
5d0331c to
ec729bb
Compare
alongubkin
marked this pull request as ready for review
October 14, 2026 17:36
alongubkin
added a commit
that referenced
this pull request
Oct 14, 2026
#1032)

Progenitor panics when an operation returns a JSON body for one success
status and an empty body for another. Refreshed full SDK specifications
expose this with HTTP202 JSON /204 empty responses. The source-owned
OpenAPI normalization now uses Progenitor’s raw streamed success
response for mixed JSON/empty operations, preserving status, headers,
body bytes and typed errors. Homogeneous typed responses remain typed;
the canonical API is unchanged.

Changing an unrelated endpoint’s response cannot fix this generator
limitation. Alternatives that pretend an empty204 is JSON fail at
runtime; removing the operation would make the full SDK incomplete.

Validation: 17 normalization/filter tests pass, including mixed versus
homogeneous responses, status/body/error preservation and idempotence.
The quota framework’s refreshed-contract integration test additionally
exercises the actual generated client against TCP202 JSON and204 empty
responses; that test belongs with the refreshed specification because
the affected operation is absent from the old main input. No generated
source lines were edited by hand.

This is a separate prerequisite for the quota framework’s refreshed full
Rust SDK. No cloud permissions, persisted data or runtime API behavior
change.

Current-head CI is green. Greptile **5/5** reviewed `2949e22bf` with no
actionable findings
([review](#1032 (comment))).

Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer
depends on the preceding PR; human merges only.

🤖 Generated with [Claude Code](https://claude.com/claude-code)

Co-authored-by: islo <sandbox@islo.dev>
alongubkin
added a commit
that referenced
this pull request
Oct 14, 2026

A deployment can continue when quota uncertainty or insufficient
scale-to-maximum headroom does not prevent its immediate work. This
layer adds the pure quota model, Fail/Warn/Unknown presentation,
deployment override setting, both CLI flags, persistence endpoints and
status/JSON visibility. Cloud checks are added by the following layers.

The model stays in `alien-preflights` behind the existing runtime-check
feature boundary; no new crate or cloud permissions are needed.
Repeatable `--quota-warning-override <identity>` downgrades only that
deployment's matching Fail to a visible Warn.
`--clear-quota-warning-overrides` explicitly clears the saved list.
Invalid or wrong-cloud identities fail before cloud work. Omission
preserves settings; empty lists clear them. Compute and override saves
are atomic. Standalone saves do not schedule work; explicit
failed-preflight and failed-update deploys request retry after
acceptance. Initial hosted settings are saved before setup, and setup
honors the claimed execution phase rather than a detail response's
displayed prior failure.

Compute blocks only when capacity certainly launched by this operation
does not fit. Initial launch uses the configured minimum;
scale-to-maximum shortfalls warn visibly with the quota identity,
shortfall and increase link. Bounds-only changes add no replacement
surge. Instance-type replacement, and effective disk changes on AWS,
count the proven rolling overlap. Late-resolved
image/identity/interrupted-rollout inputs remain a visible Unknown
warning; they never add speculative blocking surge. Observed held
capacity is credited in its original quota pool.

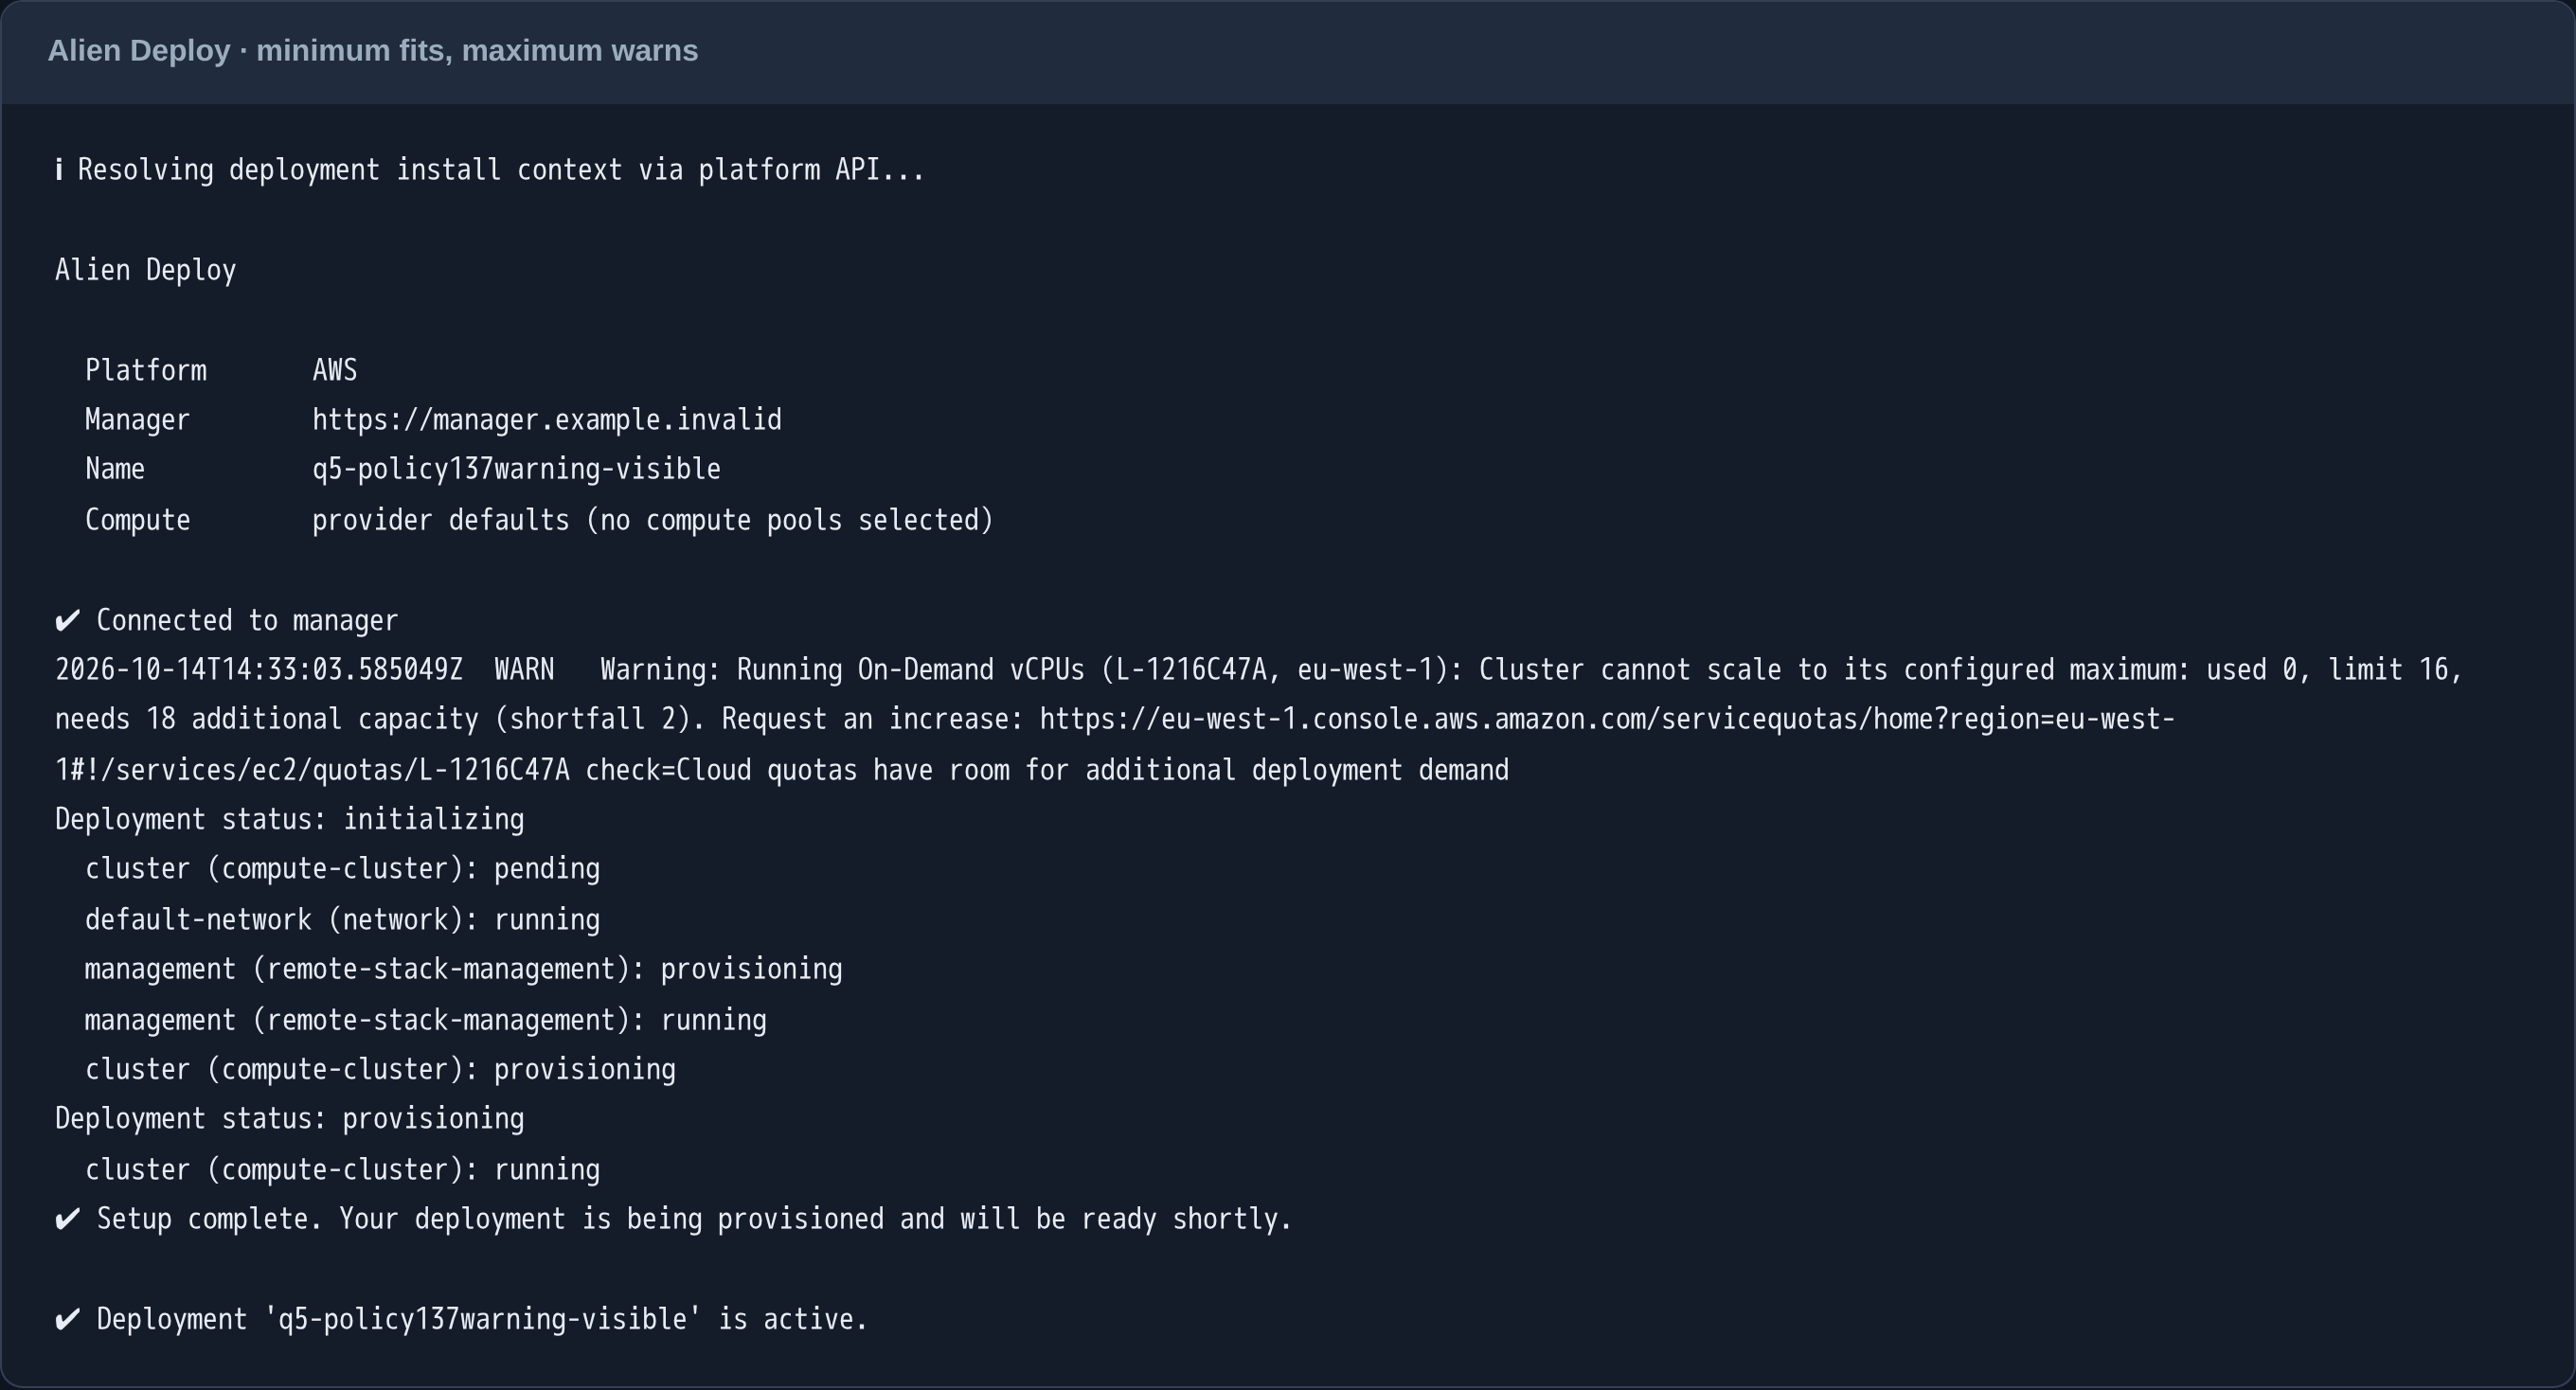
ALIEN-1506 is included here: the branded CLI now shows preflight
warnings at its default log level while preserving explicit log filters.
[Actual visible warning and successful
setup](https://raw.githubusercontent.com/alienplatform/alien/15fca237411a53a67c18ded6002234ecbac73294/pr-assets/alien-5/policy137/warning.png).
Warning callbacks remain best effort; genuine validation failures still
reject builds.

Compatibility: the new setting defaults to empty and omits empty values
on serialization. Old stored settings and errors continue to
deserialize; status/JSON makes saved overrides inspectable. Existing
protocol/controller versions are unchanged. [Parent-created deployment
update and supported mixed-version
report](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/session93-compatibility.md)
and
[cleanup](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/session93-cleanup.json)
retain the earlier integrated-feature evidence. Unknown/missing read
permissions never block.

Generated artifacts came from the supported schema/OpenAPI exporters,
`pnpm run generate:manager-rust-sdk`, `pnpm run generate:manager-api`
and `pnpm run generate:platform-api`; generated lines were not edited by
hand. ALIEN-1505 is a separate prerequisite for the refreshed full Rust
SDK contract. Execution-config roundtrips retain saved overrides and
explicit clearing.

Validation: 461 preflight library tests pass with runtime checks;
manager, OSS CLI and branded CLI compile checks pass on this layer. The
integrated command/setup HTTP suite passes 89 tests; Rust SDK 19 focused
checks, manager TypeScript wire contracts 8 and API SDK contracts 34
pass. The failed-install claim regression fails on the previous client
at PreflightsFailed and passes by reaching the first InitialSetup
checkpoint; a refusal stops before further work.

Restacked on main `3e31d392e` after #1020 merged, without duplicated
teardown changes. Current-head CI is green and Greptile **5/5** reviewed
`c3158ba21`; this PR is ready for review.

CI follow-up: all four explicit operator settings fixtures now
initialize the default override list; existing operator config suite **9
PASS**. The downstream final tree changes only these fixture defaults.
Current-head CI is green and Greptile5/5; ready for review.

Failed-update recovery:
[c3158ba](c3158ba)
allows only unlocked `update-failed` deployments to save overrides in
the atomic settings write. Saving leaves failure/retry state unchanged;
branded deploy requests an explicit retry after a successful save or
unchanged explicit override. Existing SQLite and real command HTTP
regressions fail on the prior implementation and pass after the fix.
Full manager library/HTTP suite **338 PASS**; branded up command suite
**89 PASS**, covering failed-update save/clear/refusal/unchanged
retries. No API schema changes.

Prepared head `c3158ba21` includes the framework failed-update recovery
fix. Current-head CI is green and Greptile **5/5** reviewed `c3158ba21`
with no actionable findings
([review](#1026 (comment)));
ready for review.

Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer
depends on the preceding PR; human merges only.

🤖 Generated with [Claude Code](https://claude.com/claude-code)

---------

Co-authored-by: islo <sandbox@islo.dev>
Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>
alongubkin
added a commit
that referenced
this pull request
Oct 14, 2026
AWS setup and capacity updates now compare added demand with applied
quotas before provisioning: VPCs, internet gateways, Elastic IPs,
On-Demand EC2 vCPUs by quota family, and Lambda reserved concurrency.
Covered creation races retain the same typed quota identity, scope and
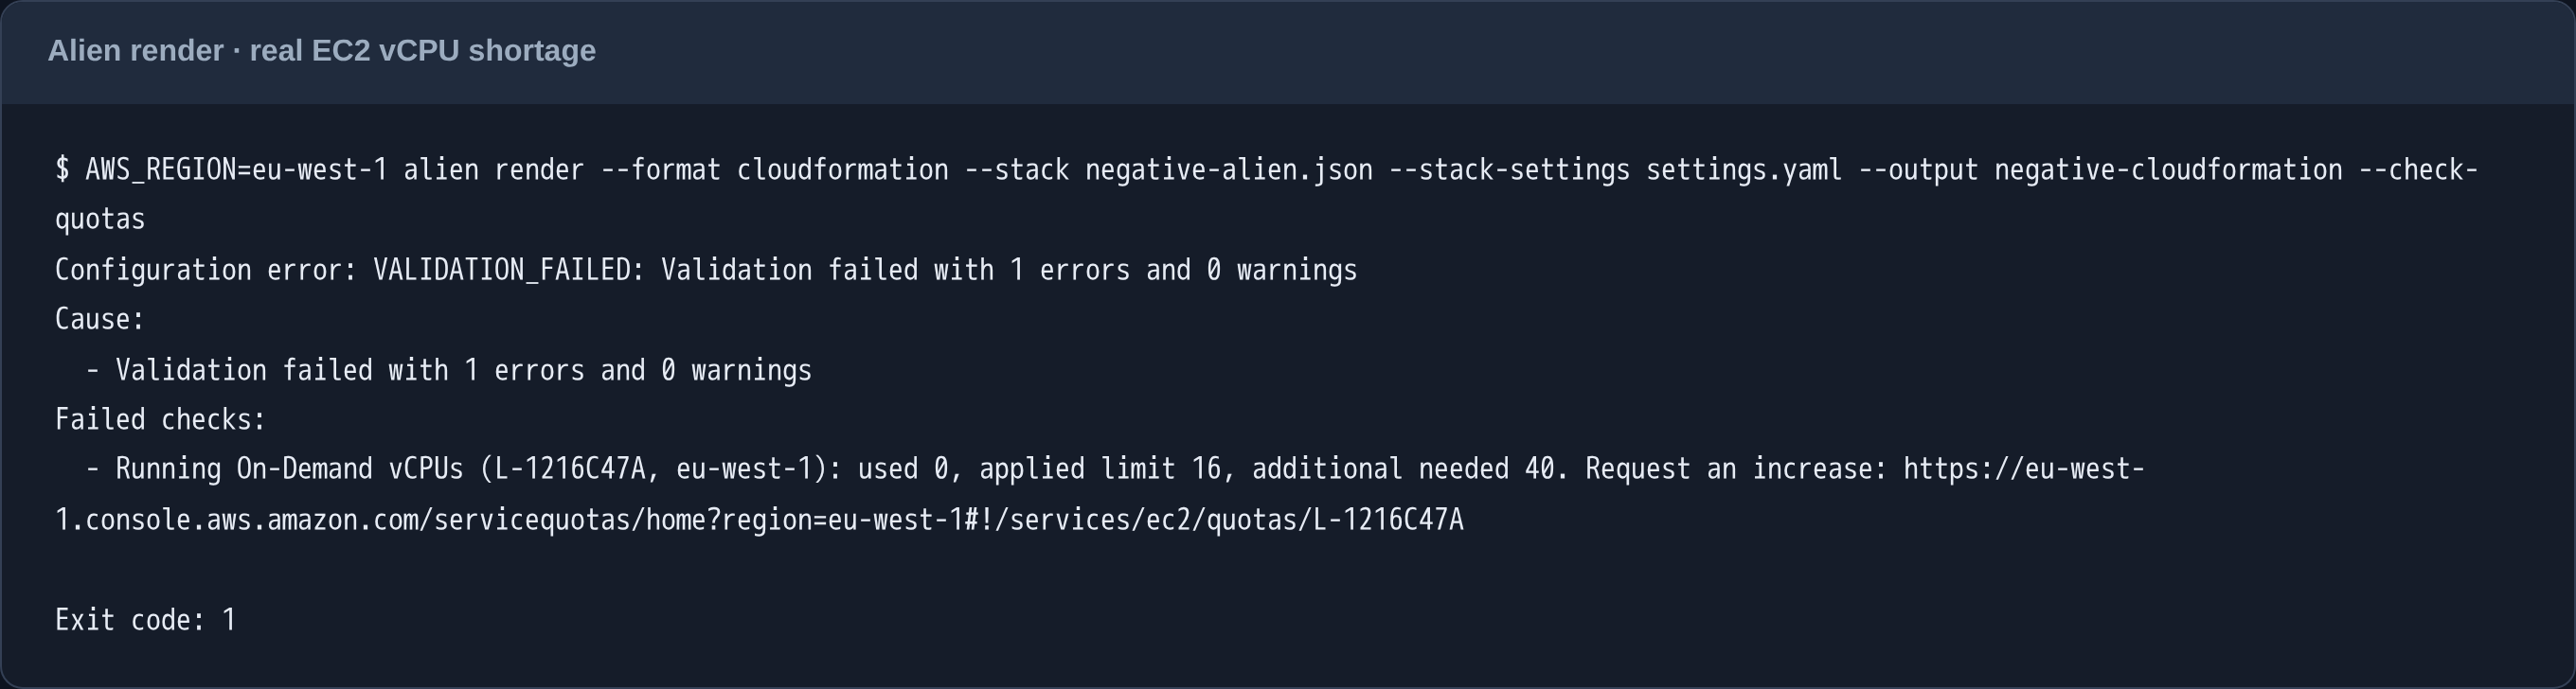
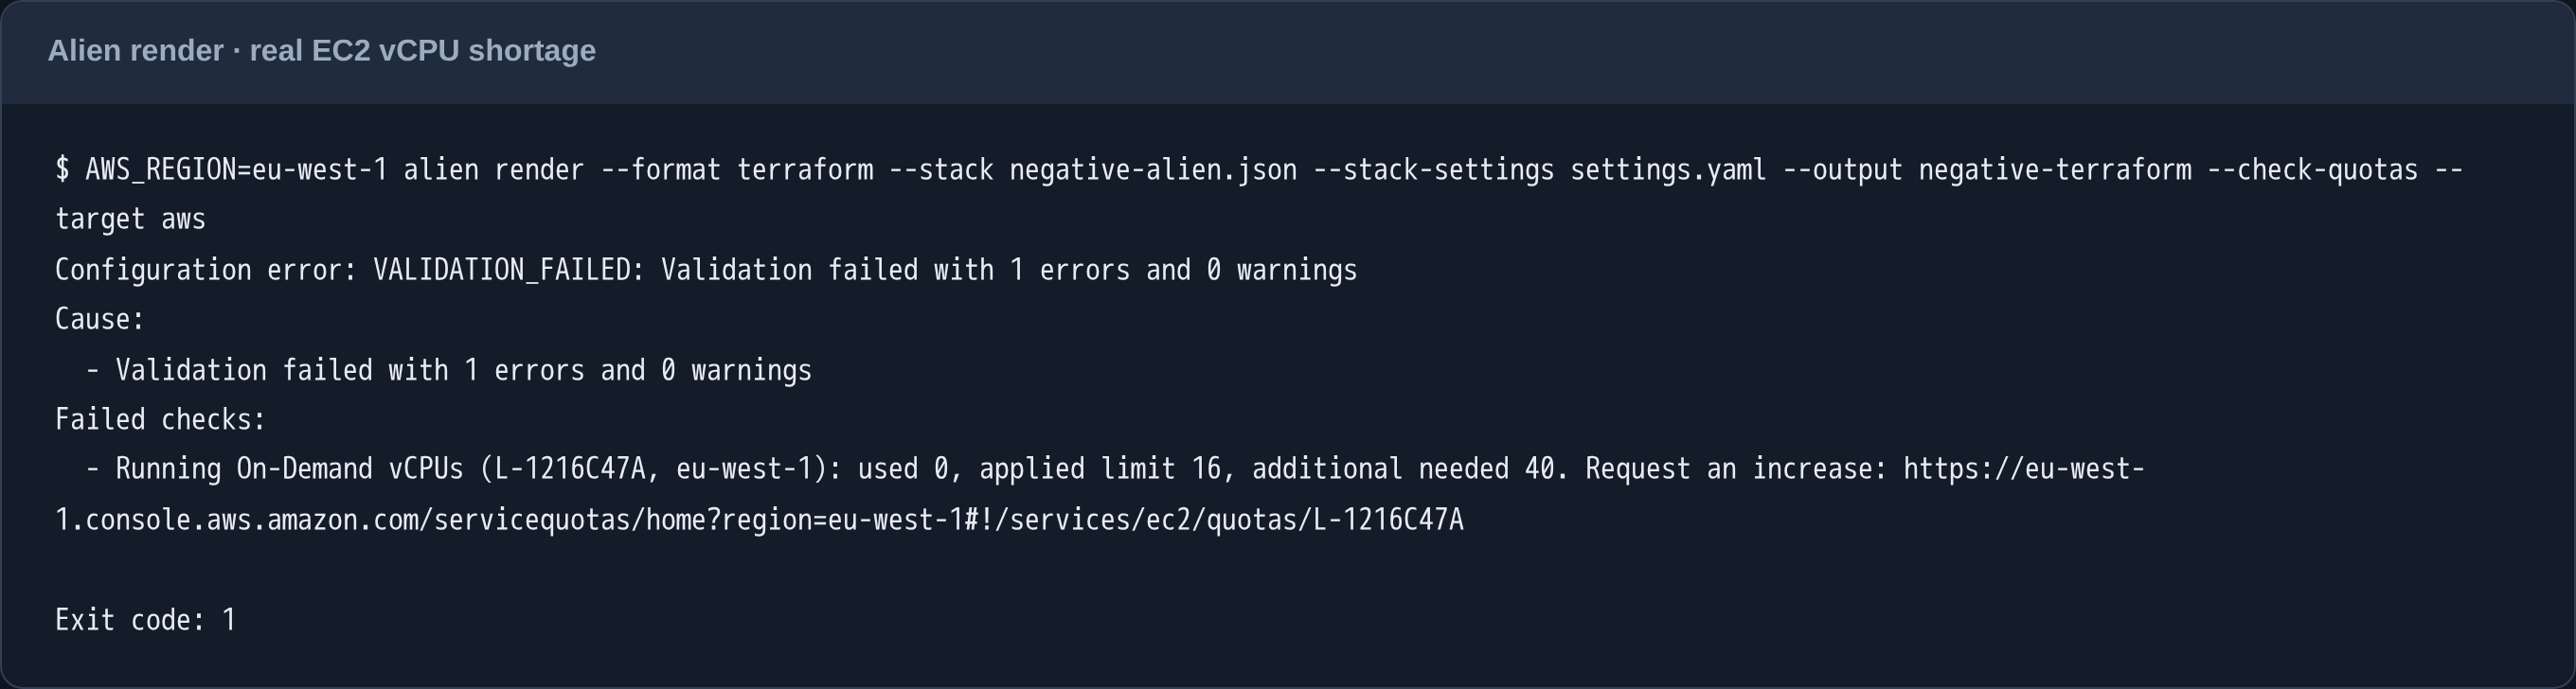
increase link. `alien render --check-quotas` checks new AWS
CloudFormation/Terraform installations before writing artifacts.

Usage follows provider semantics: EC2 counts pending/running On-Demand
instances and excludes Spot; EIPs preserve service-managed/BYOIP
exclusions. Capacity checks distinguish immediate launch demand from
maximum headroom, crediting observed held capacity. Low-account Lambda
reservation floors that cannot be established safely produce Unknown;
zero reservations consume no capacity. NAT uses the existing
resolved-zone controller guard and typed mapping. Early runtime NAT
returns Unknown when placement is unresolved; adding a core placement
field was disproportionate and has been dropped.

Permissions: compute adds `servicequotas:GetServiceQuota` (applied quota
values) and `ec2:DescribeInstanceTypes` (public hardware metadata), plus
the separately reviewed `ec2:DescribeSecurityGroups` discovery repair
from #1022. Worker adds `lambda:GetAccountSettings` for account capacity
and `lambda:GetFunctionConcurrency` scoped to existing deployment
function ARNs for reservation credit. Existing EC2 network/instance
describes supply inventory; no CloudWatch or customer telemetry access
is added.

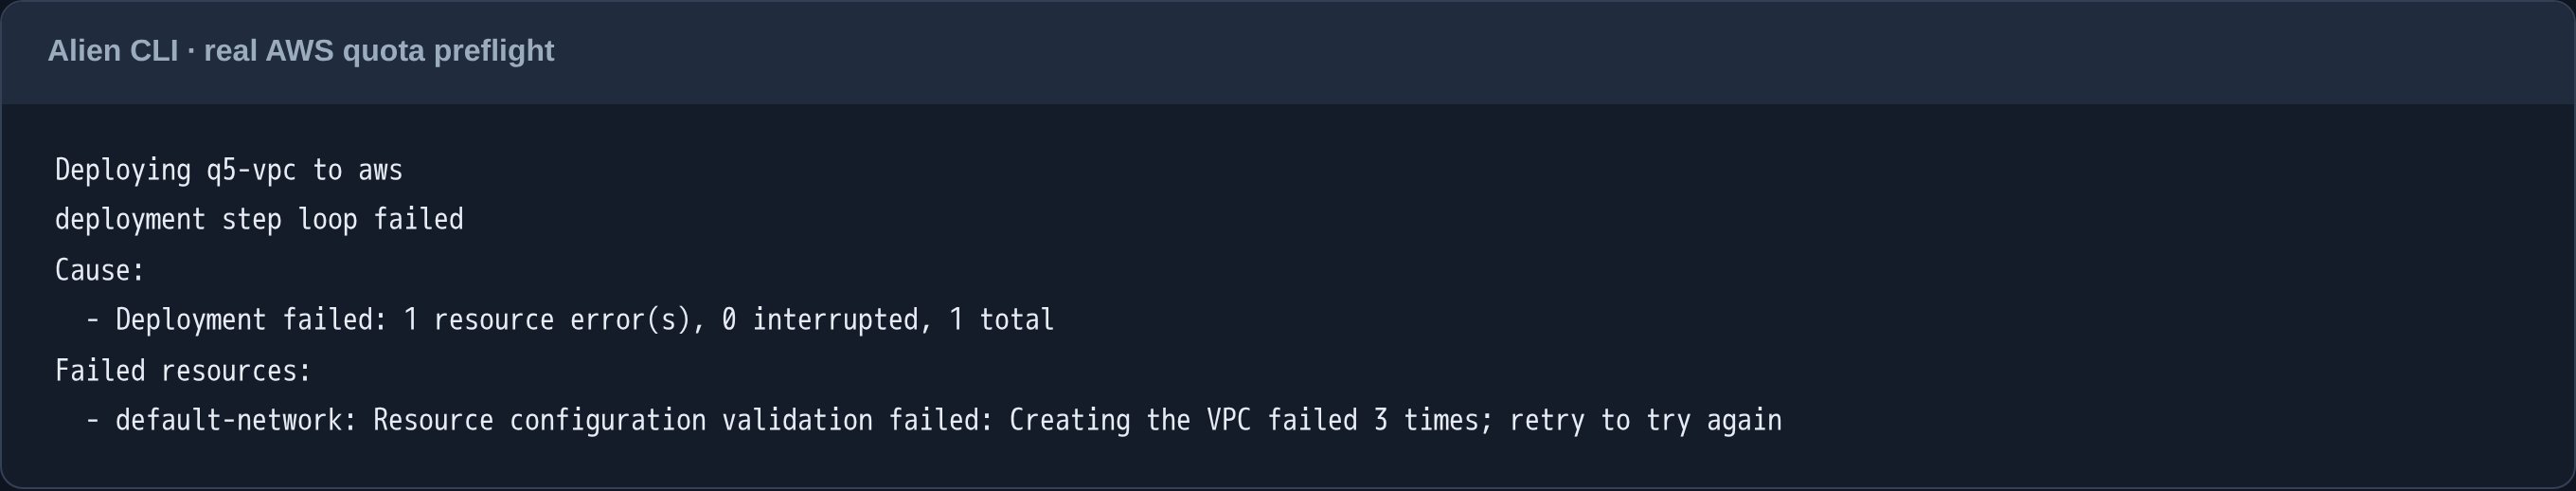
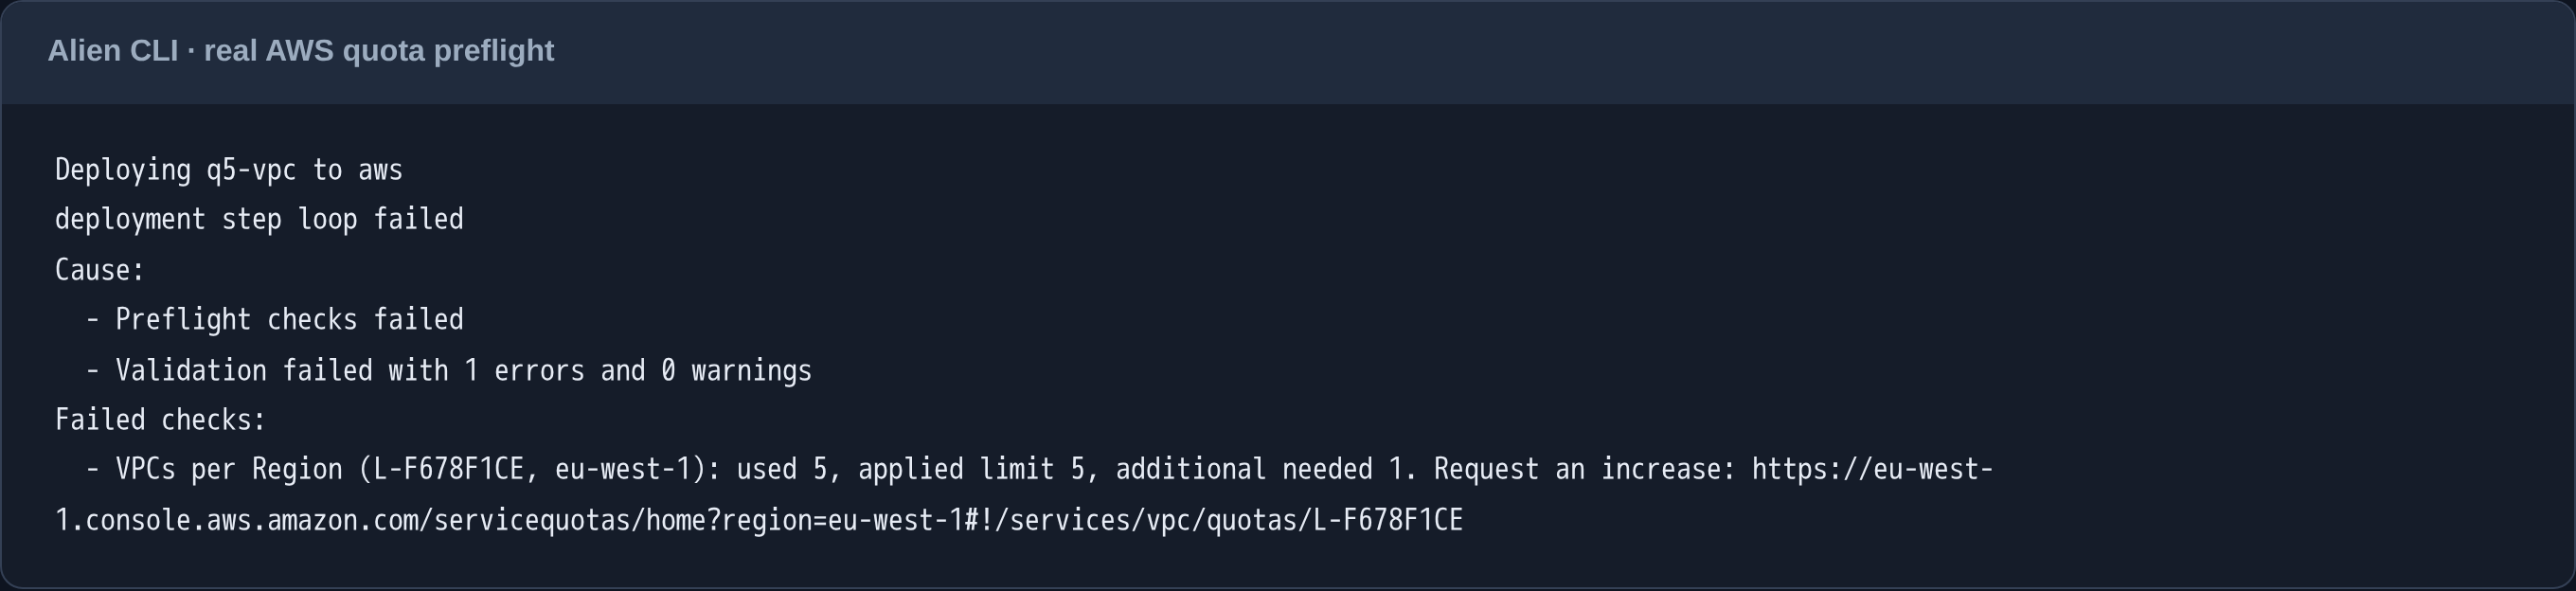
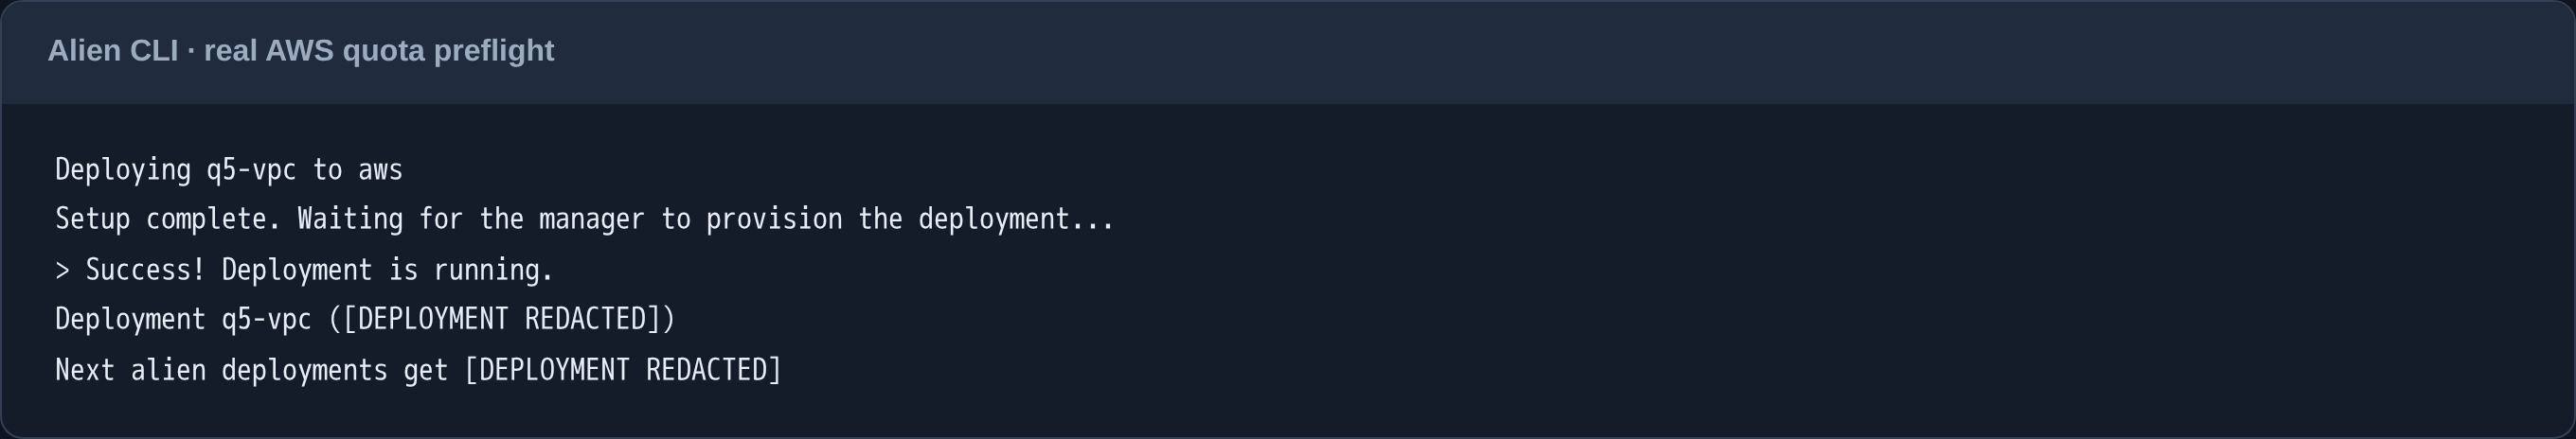
Existing real-cloud evidence, retained from #1010:

- [VPC
before](https://raw.githubusercontent.com/alienplatform/alien/ef7073cba/pr-assets/alien-5/aws-vpc-cli-before-negative.png),
[early
rejection](https://raw.githubusercontent.com/alienplatform/alien/ef7073cba/pr-assets/alien-5/aws-vpc-cli-negative.png),
[positive](https://raw.githubusercontent.com/alienplatform/alien/66b6fde2c/pr-assets/alien-5/aws-vpc-cli-positive.png).
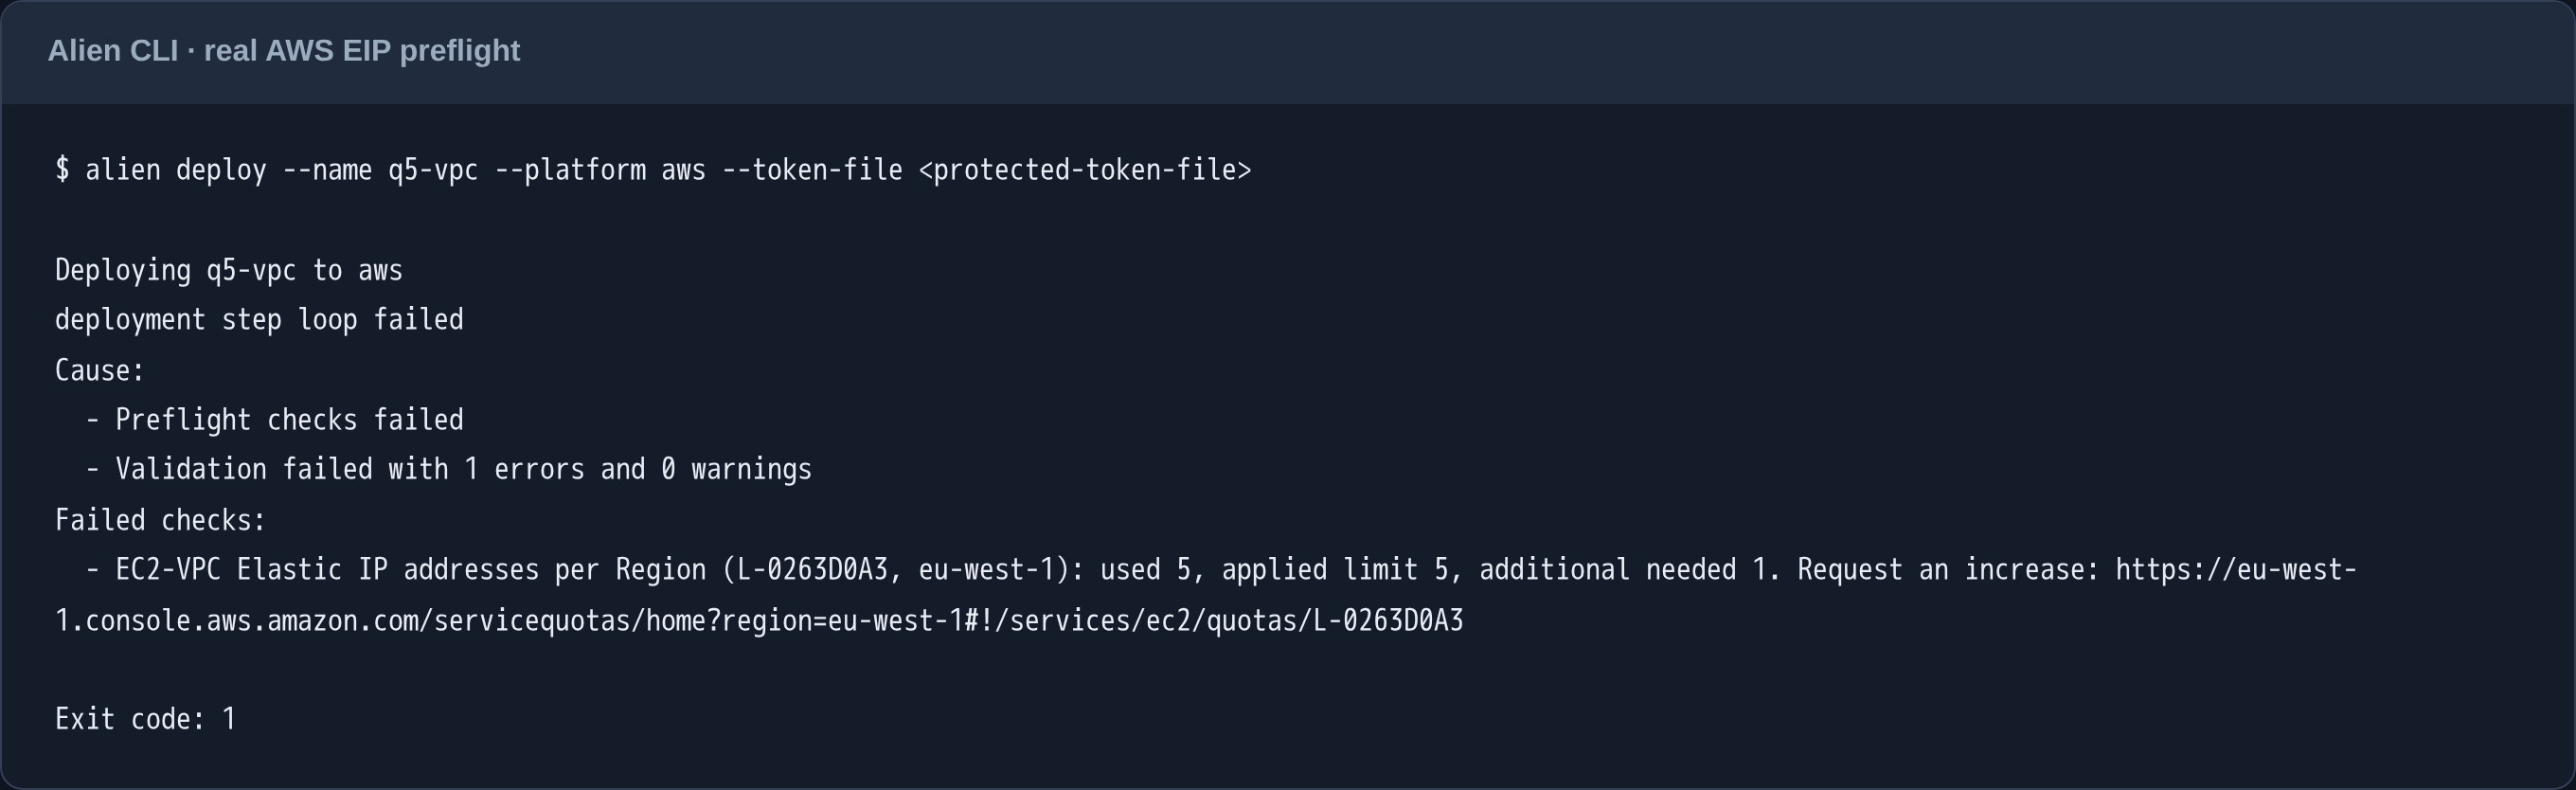
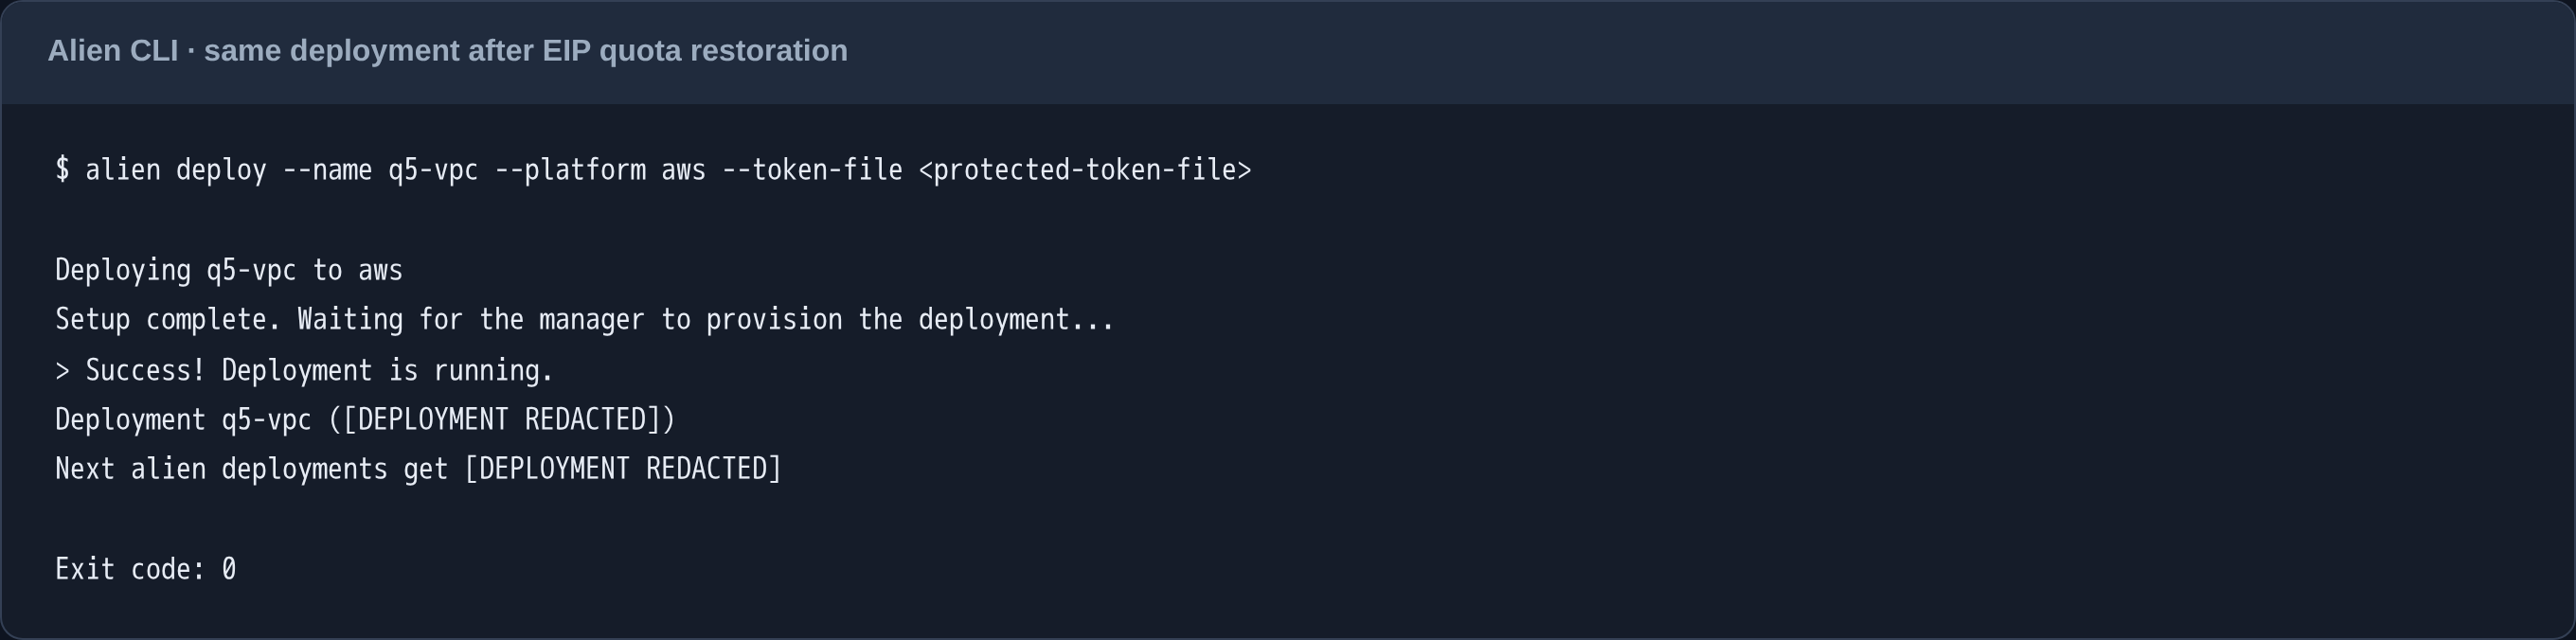
- [EIP early
rejection](https://raw.githubusercontent.com/alienplatform/alien/d4741d191/pr-assets/alien-5/aws-eip-cli-negative.png),
[same-record
positive](https://raw.githubusercontent.com/alienplatform/alien/d4741d191/pr-assets/alien-5/aws-eip-cli-positive.png),
[exact provider sets and
cleanup](https://raw.githubusercontent.com/alienplatform/alien/d4741d191/pr-assets/alien-5/aws-eip-cleanup.json).
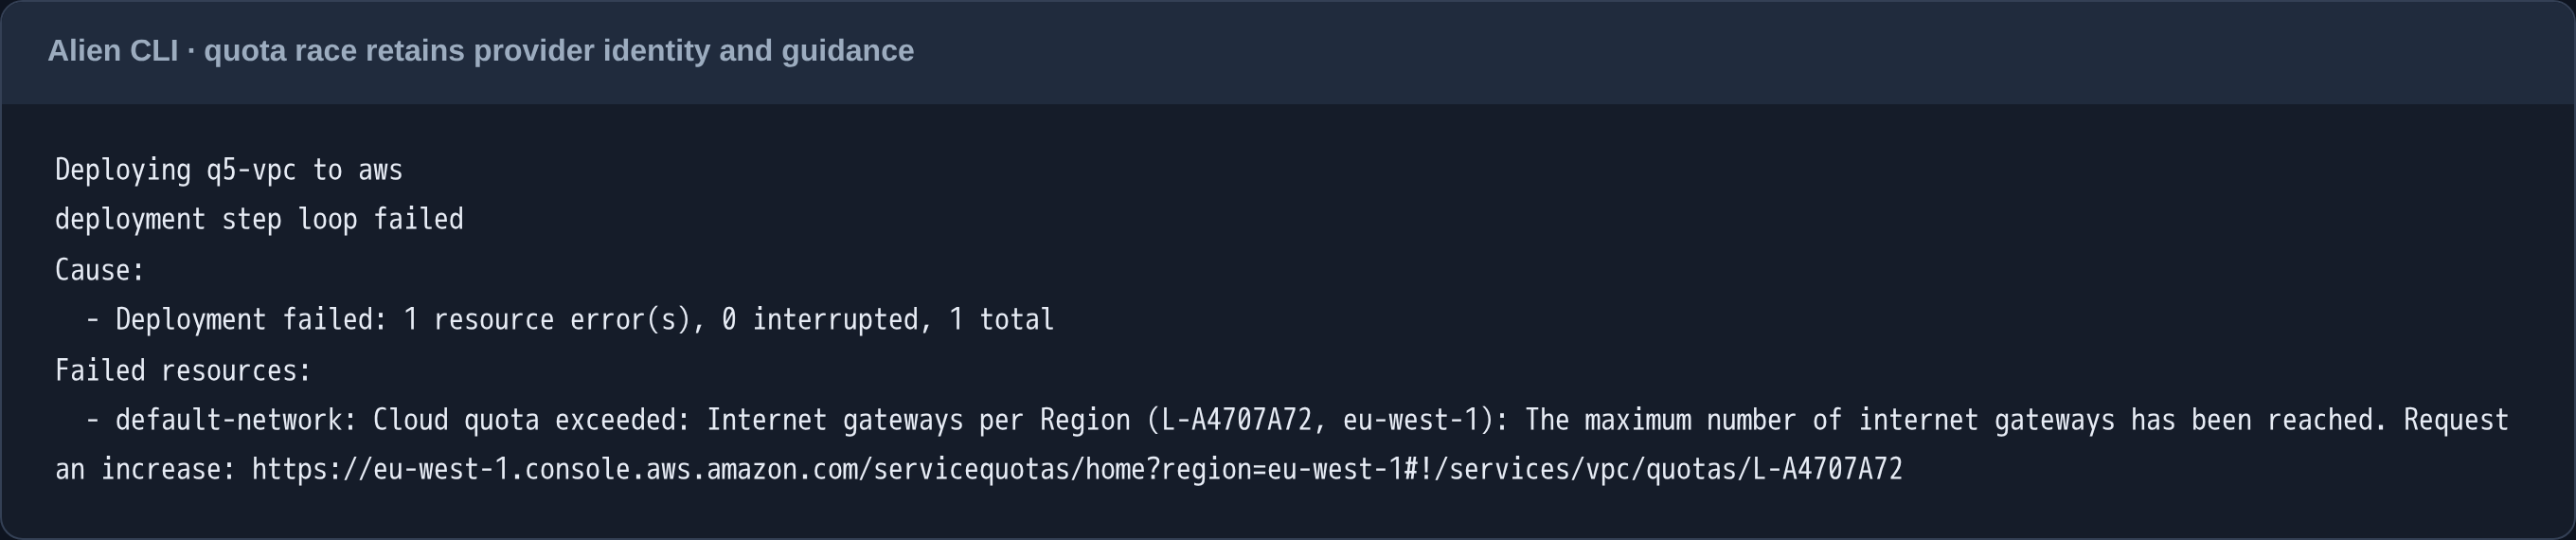
- [Post-preflight IGW
race](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/aws-igw-race-cli-after.png)
and
[cleanup](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/aws-igw-race-cleanup.json).
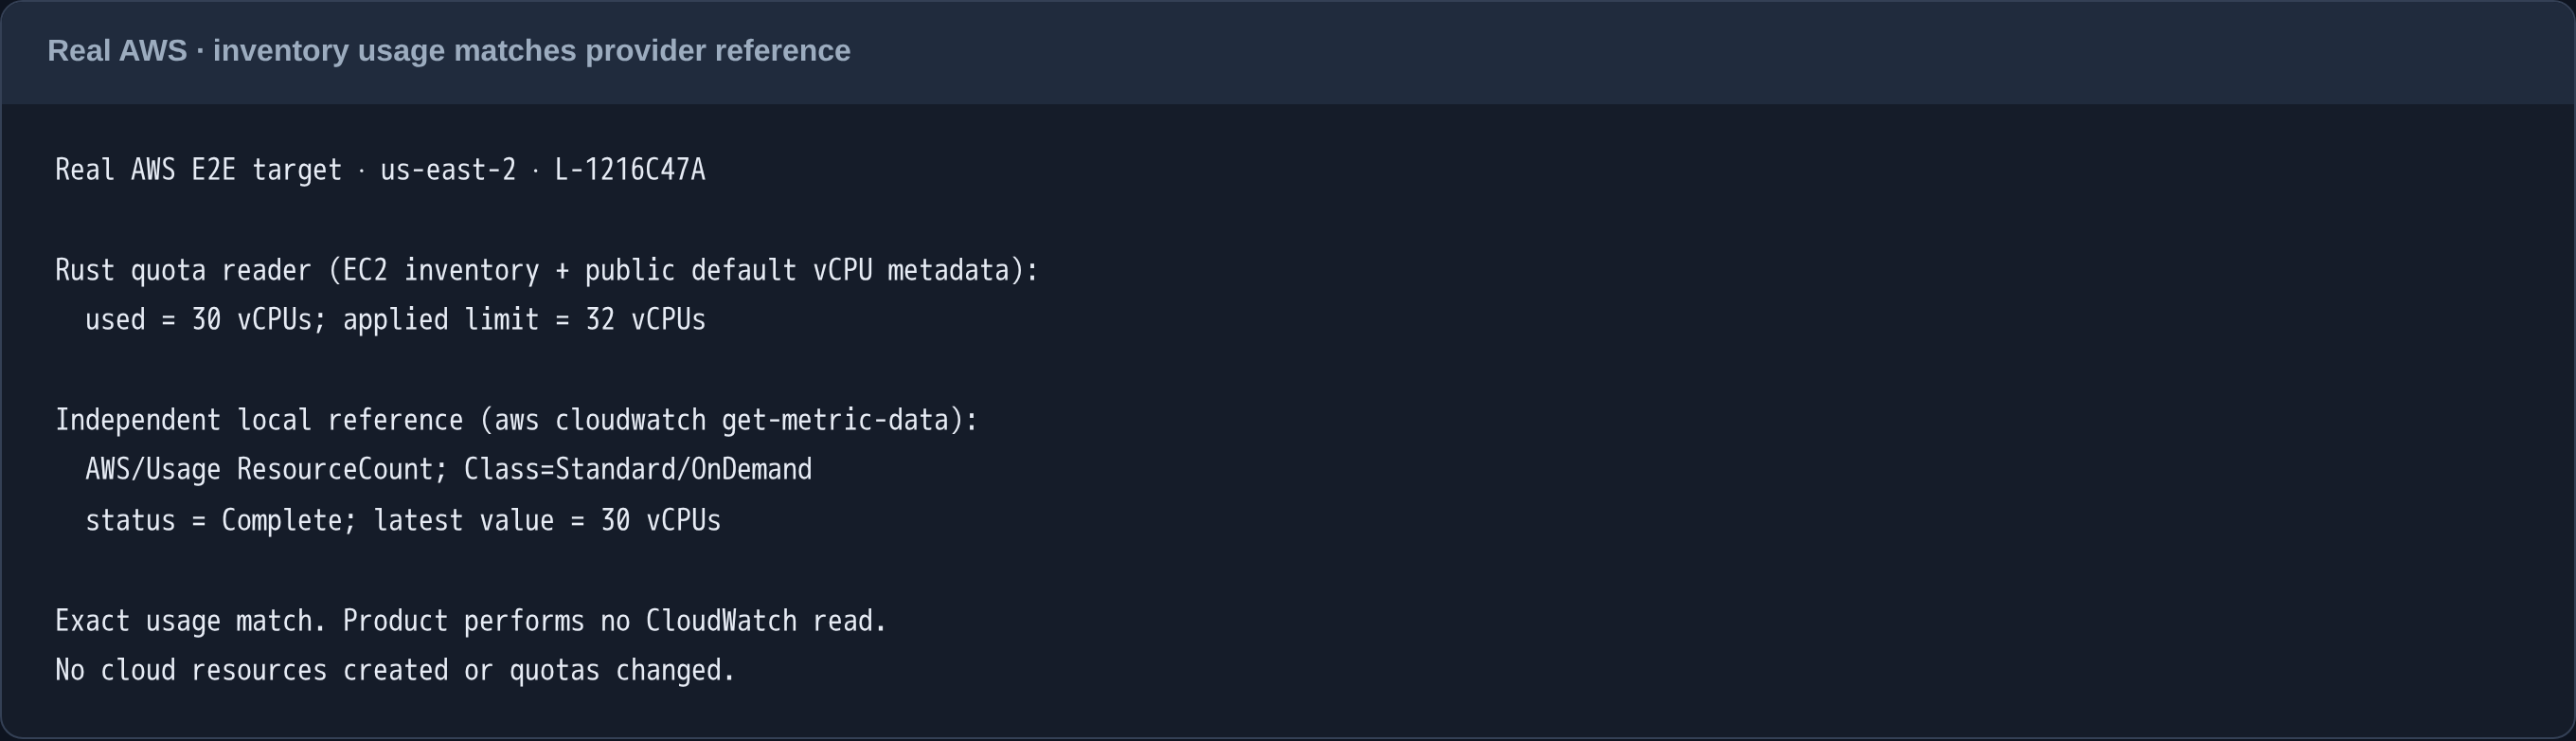
- [EC2 usage
comparison](https://raw.githubusercontent.com/alienplatform/alien/68411ae2f/pr-assets/alien-5/aws-vcpu-usage-comparison.png):
inventory30 matches the independent provider reference30.
[CloudFormation
negative](https://raw.githubusercontent.com/alienplatform/alien/68411ae2f/pr-assets/alien-5/aws-vcpu-cfn-negative.png)
and [Terraform
negative](https://raw.githubusercontent.com/alienplatform/alien/68411ae2f/pr-assets/alien-5/aws-vcpu-tf-negative.png)
reject before output files; the standalone small compute fixture lacks
an emitter, so it is not a successful deployment control.
- [Missing-read CLI render
controls](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/session94-missing-read-render.md):
both formats warn and render successfully; temporary reader role
deleted.

Compatibility: unavailable quota reads are non-blocking Unknown,
including installed roles missing new grants. No Stack placement or
controller-state fields are introduced. Raw `terraform apply` and
CloudFormation execution cannot run Rust runtime checks; use the
optional render precheck, with native provider errors remaining possible
after rendering. Lambda low-account fixed100 historical screenshots are
superseded by the safe Unknown behavior; no new Lambda deployment/race
claim is made here.

Compute blocks only when capacity certainly launched by this operation
does not fit. Initial launch uses the configured minimum;
scale-to-maximum shortfalls warn visibly with the quota identity,
shortfall and increase link. Bounds-only changes add no replacement
surge. Instance-type replacement, and effective disk changes on AWS,
count the proven rolling overlap. Late-resolved
image/identity/interrupted-rollout inputs remain a visible Unknown
warning; they never add speculative blocking surge. Observed held
capacity is credited in its original quota pool.

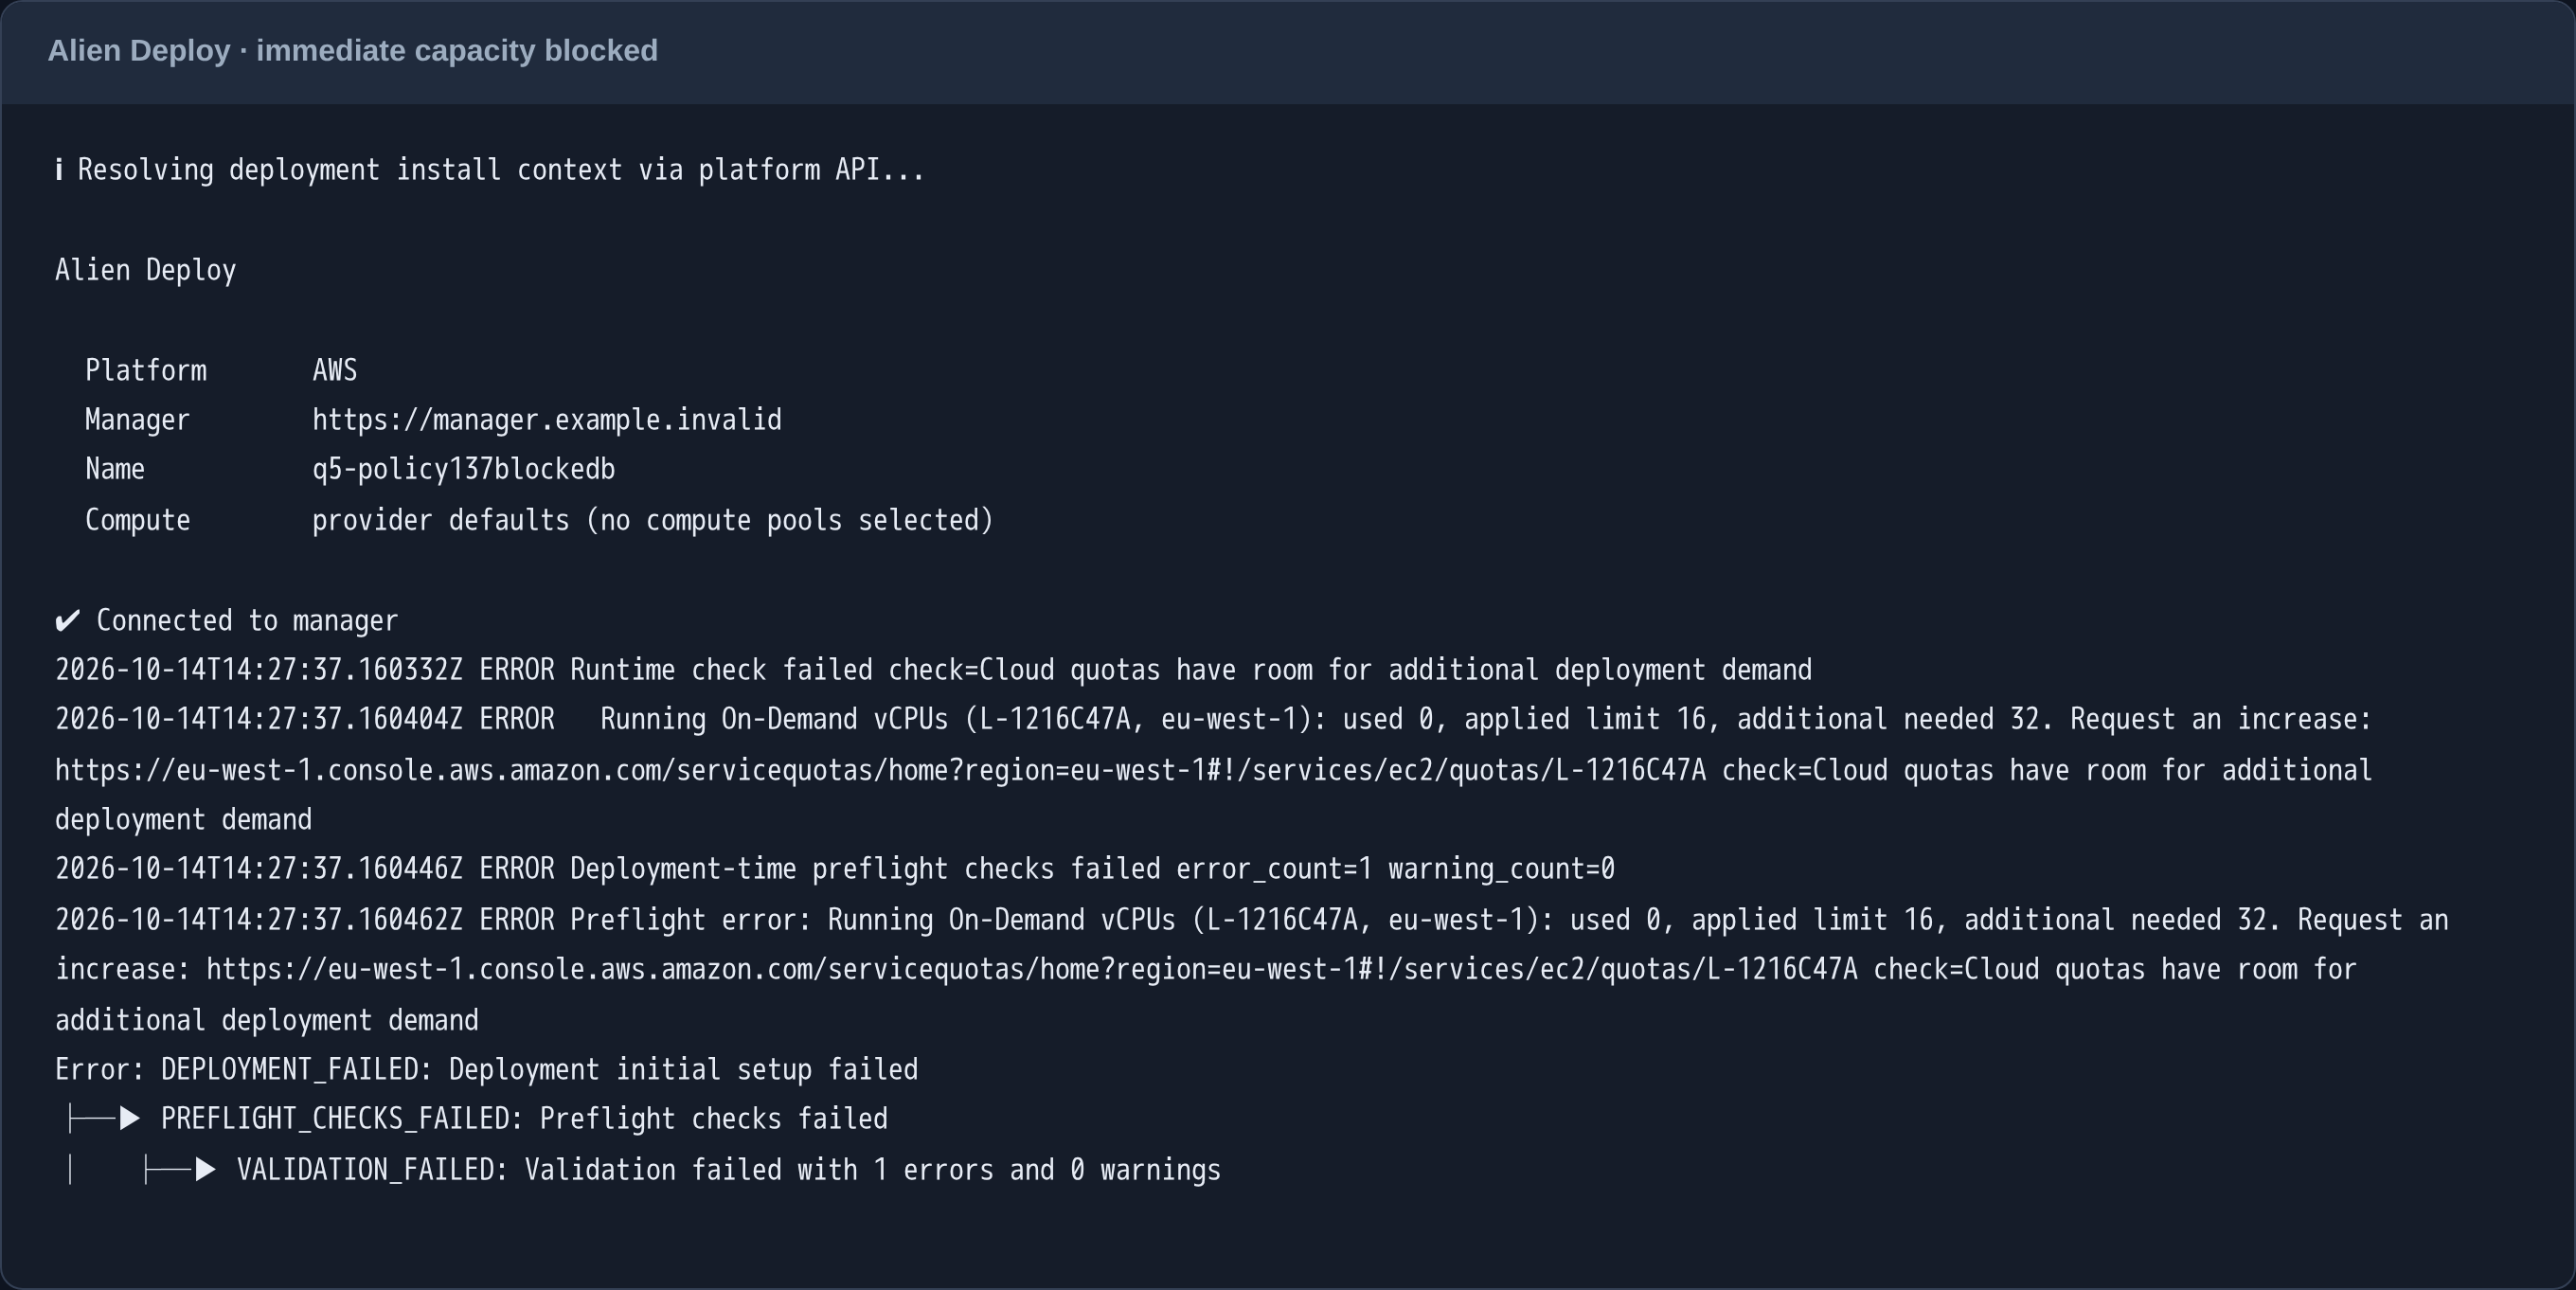
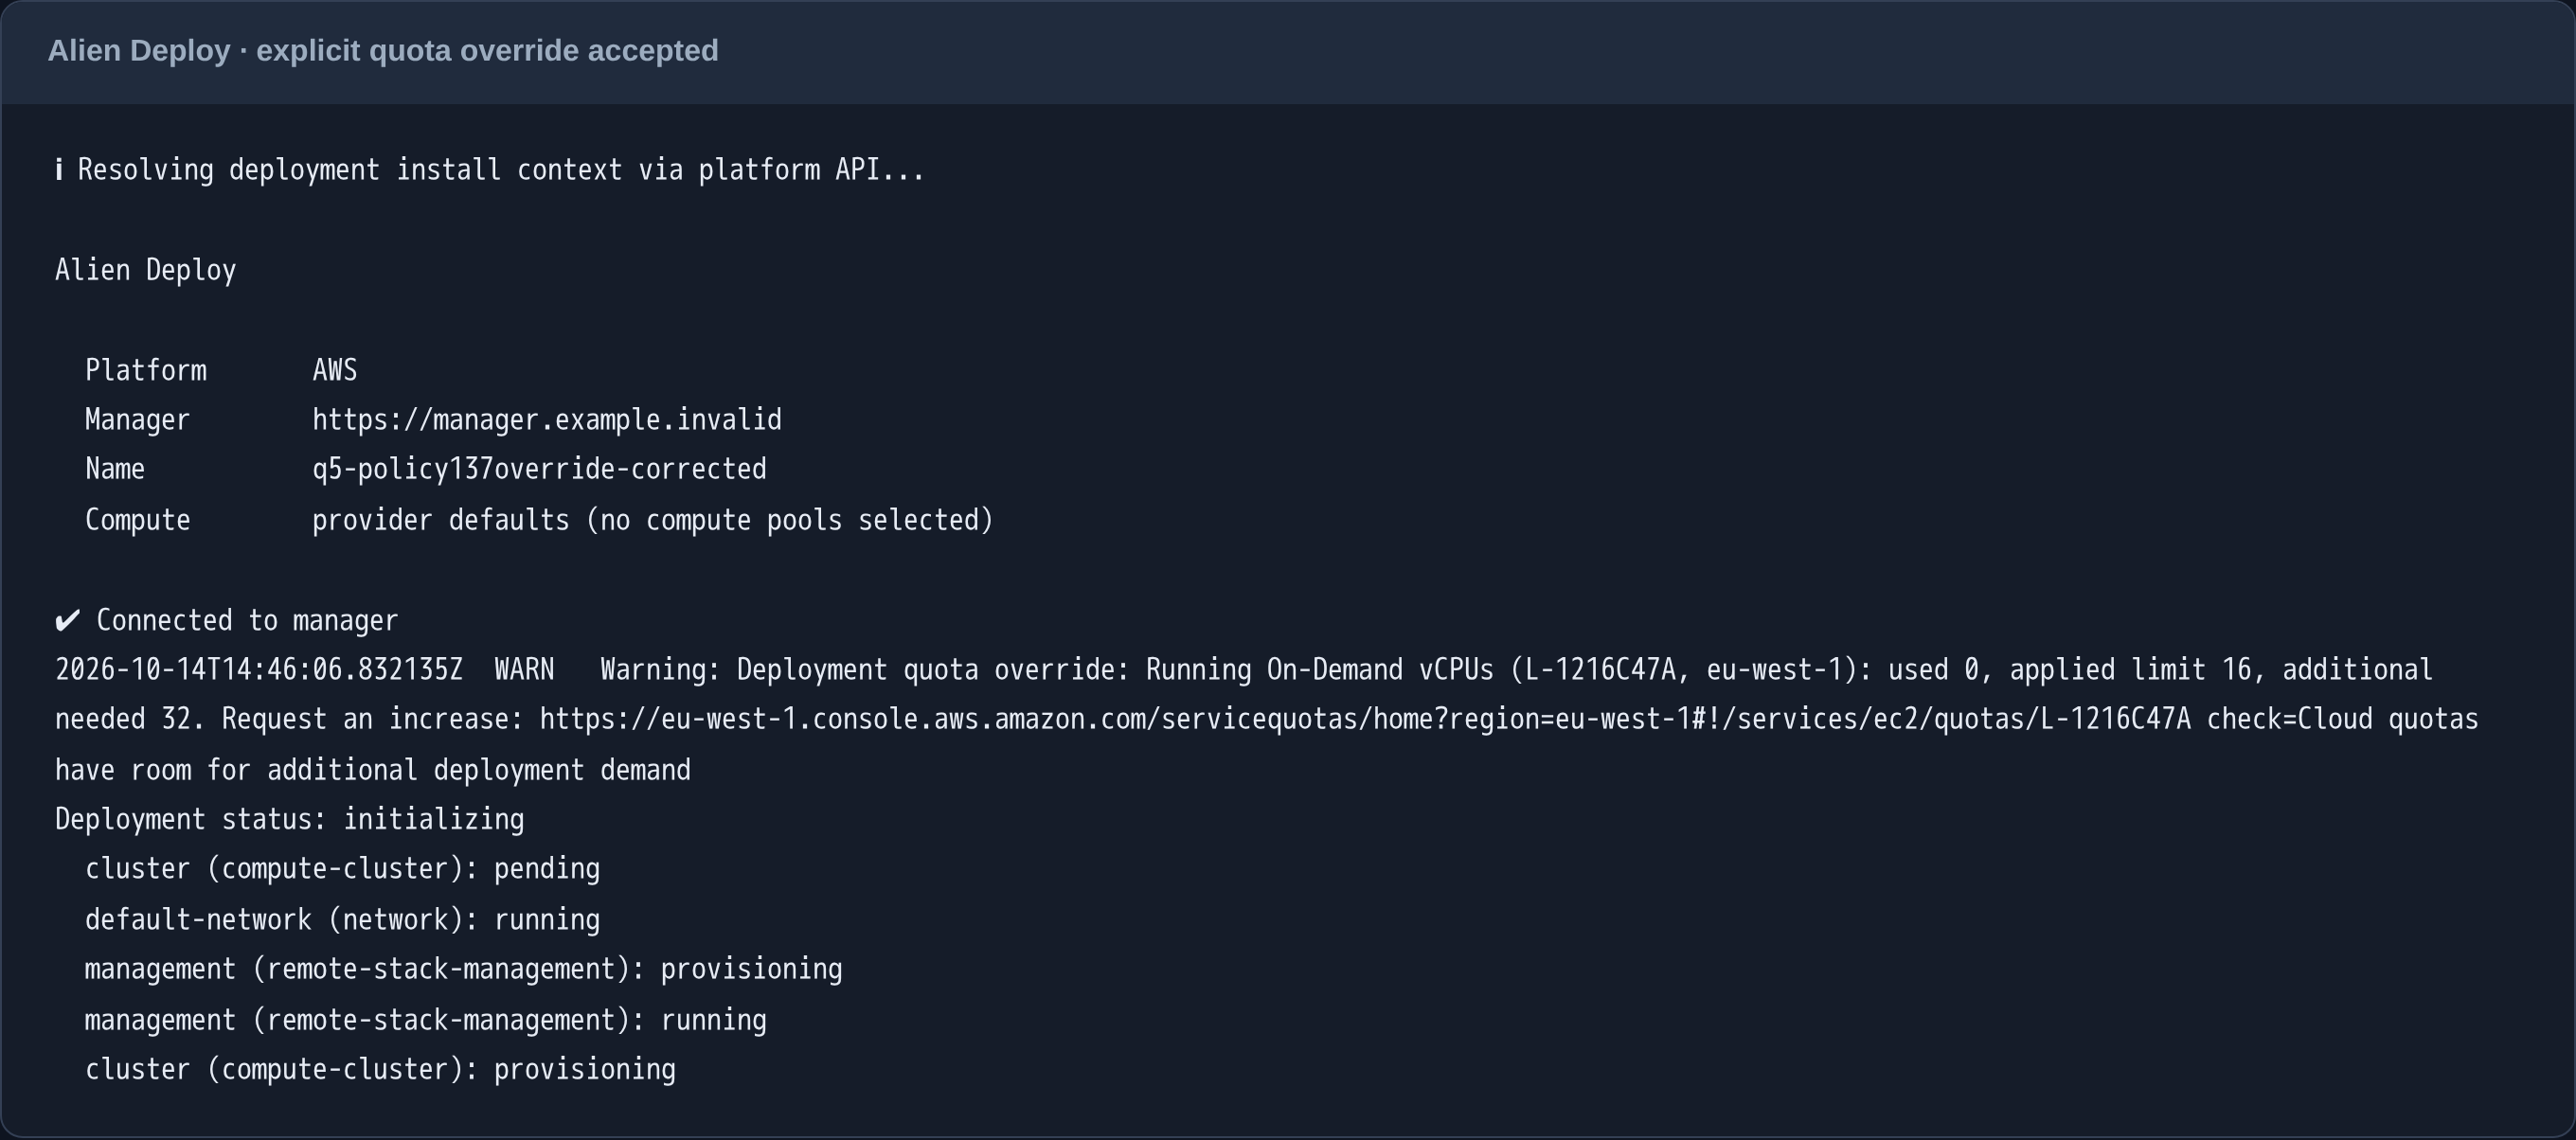
New minimal policy controls: [min fits / max short warning and active
deployment](https://raw.githubusercontent.com/alienplatform/alien/15fca237411a53a67c18ded6002234ecbac73294/pr-assets/alien-5/policy137/warning.png),
[immediate capacity
rejection](https://raw.githubusercontent.com/alienplatform/alien/15fca237411a53a67c18ded6002234ecbac73294/pr-assets/alien-5/policy137/blocked.png),
[saved override
acceptance](https://raw.githubusercontent.com/alienplatform/alien/15fca237411a53a67c18ded6002234ecbac73294/pr-assets/alien-5/policy137/override.png),
and [inputs, max-only update, limitations and
cleanup](https://raw.githubusercontent.com/alienplatform/alien/15fca237411a53a67c18ded6002234ecbac73294/pr-assets/alien-5/policy137/proof.md).
Applied Standard quota16, usage0: m7i.large min0/max9 warns at18;
m7i.4xlarge min2/max2 blocks at32. Max-only9→10 reaches running with
current0/desired0. Override setup is deliberately stopped before ASG/VM
creation; this proves policy acceptance, not successful over-quota fleet
deployment. All owned resources were removed; no VM launched.

Layer validation: 491 preflight library tests pass, including
max-only/surge/disk controls and a stalled HTTP server that expires to
non-blocking Unknown. This retains the fix for [Greptile’s timeout
finding](#1027 (comment)).

Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer
depends on the preceding PR; human merges only.

The shared NAT observation bounds all reads/pages to 15 seconds and
returns Unknown on expiry. Unchanged running Lambda reservations make no
quota read, matching the controller’s write behavior. Render uses the
runtime runner to validate/apply saved overrides; direct EIP/NAT guards
emit explicit warnings for accepted identities. Parent regressions fail;
the fixed preflight library (491 tests), AWS network suite (86 tests; 1
existing live-credential test ignored), and full render command suite (4
tests) pass.

Current head `cb642001f`: **CI green, Greptile 5/5, mergeable and ready
for review**
([review](#1027 (comment))).

🤖 Generated with [Claude Code](https://claude.com/claude-code)

---------

Co-authored-by: islo <sandbox@islo.dev>
Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>
alongubkin
added a commit
that referenced
this pull request
Oct 14, 2026
GCP deployments now check regional/family CPU and supported GPU
capacity, project custom roles including soft-deleted roles, and service
accounts against applied limits. Demand comes from resource
configuration, separates immediate launches from maximum headroom, and
credits only proven held identities. Desired role IDs matching this
deployment’s own soft-deleted roles are undeleted and do not consume a
new role slot. Explicit custom-role/service-account capacity failures
map to the same typed project quota guidance; ordinary throttling
retains provider retry behavior.

Project limits use Cloud Quotas and Service Usage applied values;
regional Compute responses supply provider usage. IAM metadata lists
paginate completely. Service accounts include disabled/default accounts;
partial, duplicate or missing identities yield Unknown. Cloud Quotas
does not supply all-regions usage on the observed target, so readable
all-regions limits without usage remain Unknown. Unresolved dimensioned
GPU variants also remain Unknown.

Setup enables `cloudquotas.googleapis.com` through existing service
activation, including Terraform setup, and both test-infrastructure
modules declare it. Older setup imports and installed stacks without
that optional activation keep it absent; disabled or denied reads warn
with an enable/API-permission hint rather than blocking updates.

Permissions: `compute.regions.get`, `compute.projects.get` and
`cloudquotas.quotas.get` in project-scoped provisioning read
quota/capacity metadata. Service-account provision/management/heartbeat
sets grant project `iam.serviceAccounts.list` for complete identity
inventory; resource-scoped viewer grants cannot list project inventory.
`serviceusage.quotas.get` reads project applied IAM limits through a
narrow shared metadata role; that role is included in demand. Existing
IAM custom-role metadata reads are reused. No token/key/customer-content
or broad telemetry access is added.

Existing public-safe implementation/read evidence and exact limitations
are retained in
[#1010](#1010): applied
CPU/GPU all-regions limits360/360; A2 CPU12/A100 GPU1 controls;
paginated IAM identity equivalence and two-probe create/delete counting;
custom-role capacity response replay. These are existing
integrated-feature controls, not new runs on the split commit. Do not
interpret a parent accepting a min0/max2 configuration as a late GPU
quota failure; no GPU VM was launched. No new parent/race/entry-point
claim is added by this split.

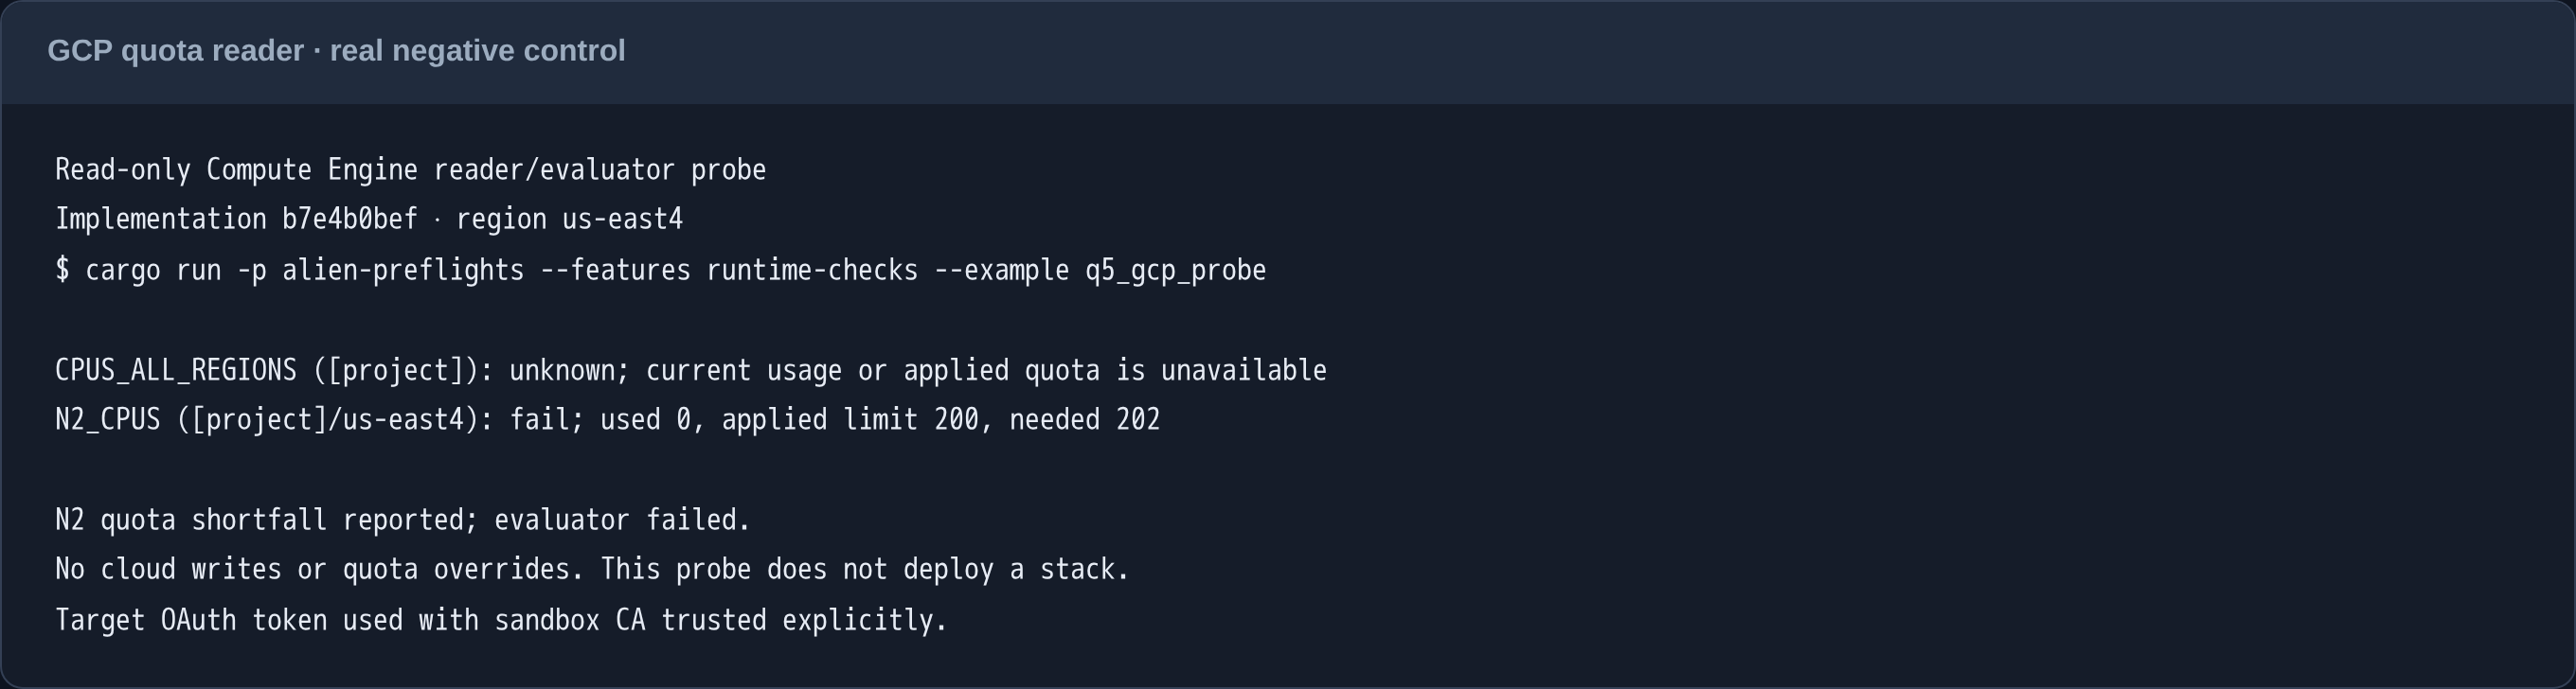
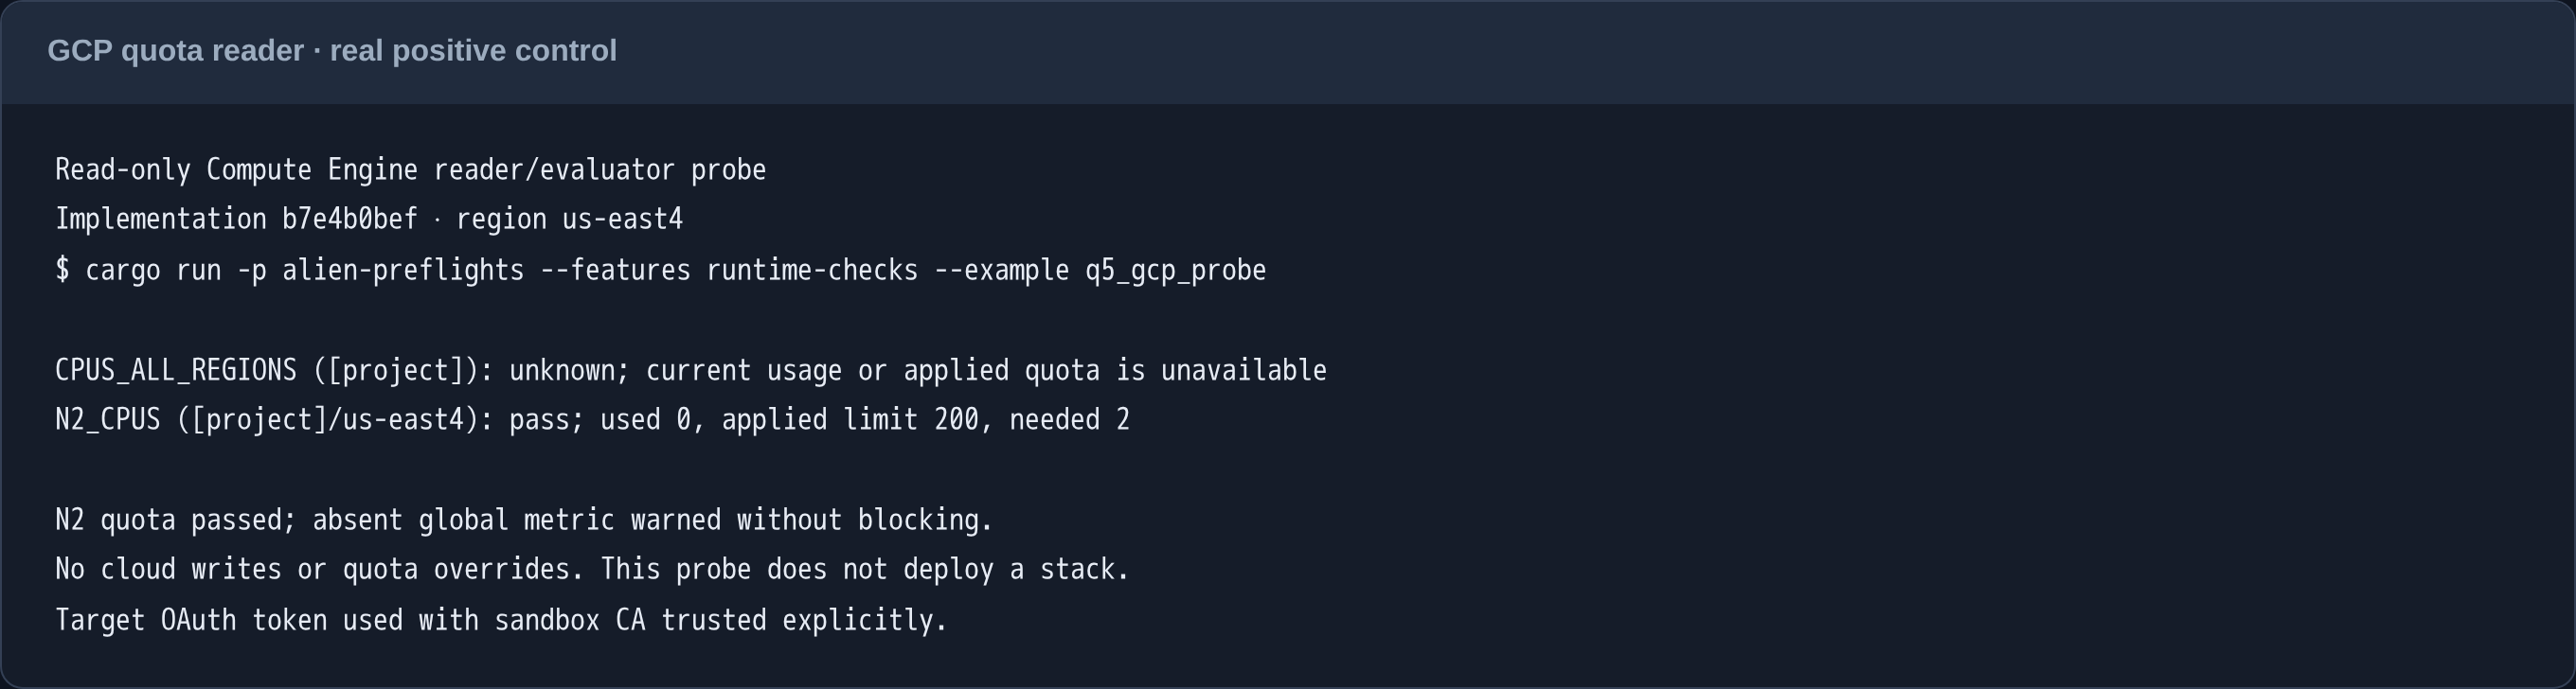
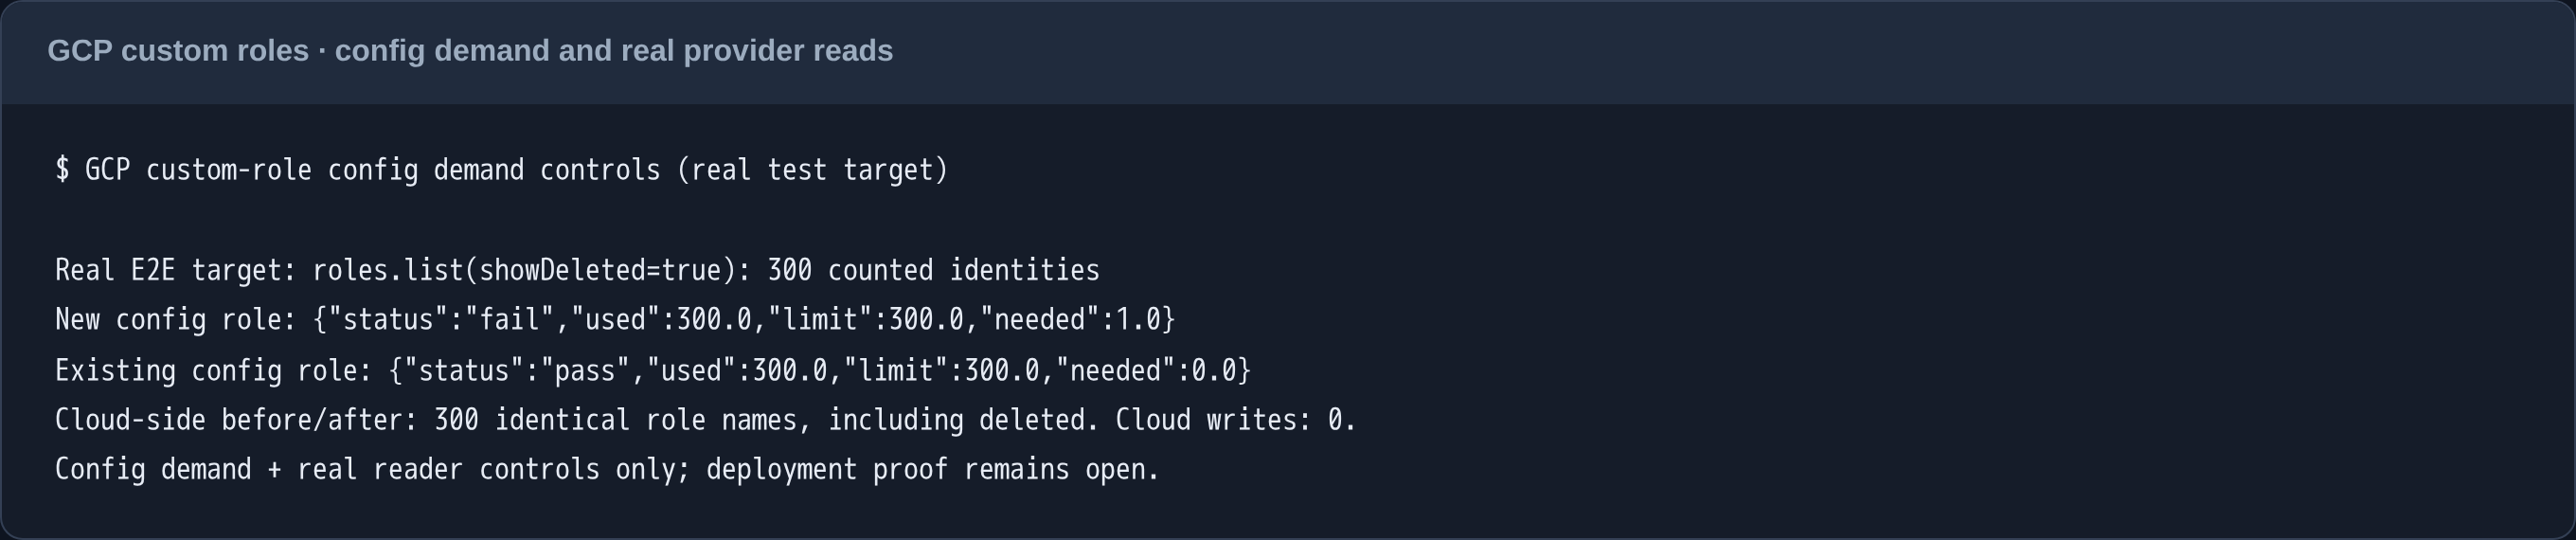
[Regional CPU
negative](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/gcp-cpu-reader/negative.png),
[positive reader
control](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/gcp-cpu-reader/control.png),
and [custom-role config
controls](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/custom-roles-config-controls.png)
show the existing read/config evidence. All these controls left provider
inventories unchanged and created no resources.

Compatibility: no persisted or SDK schema fields change in this layer.
Missing management-role quota reads produce non-blocking Unknown. Old
GCP handoff import and subsequent mutation regression coverage retain
ownership validation. The supported generator and generated-output diff
both passed in [feature
CI38534727697](https://github.com/alienplatform/alien/actions/runs/38534727697);
current-head CI and review also pass.

Compute blocks only when capacity certainly launched by this operation
does not fit. Initial launch uses the configured minimum;
scale-to-maximum shortfalls warn visibly with the quota identity,
shortfall and increase link. Bounds-only changes add no replacement
surge. Instance-type replacement, and effective disk changes on AWS,
count the proven rolling overlap. Late-resolved
image/identity/interrupted-rollout inputs remain a visible Unknown
warning; they never add speculative blocking surge. Observed held
capacity is credited in its original quota pool.

Layer validation: 518 preflight library tests pass. Read-only policy
control: regional CPUS4/200 and N2_CPUS0/200. No new cloud resources or
quota overrides were needed.

Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer
depends on the preceding PR; human merges only.

Service Usage metric requests use `view=FULL` to receive applied quota
buckets/effective limits. The missing-query parent regression fails; all
5 relevant wire tests pass, including denied reads.

Current head `1d7ab07ce`: **CI green, Greptile 5/5, mergeable and ready
for review**
([review](#1028 (comment))).

🤖 Generated with [Claude Code](https://claude.com/claude-code)

---------

Co-authored-by: islo <sandbox@islo.dev>
Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>
alongubkin
added a commit
that referenced
this pull request
Oct 14, 2026
Azure ComputeCluster deployments now check applied total regional and
per-family cores and subscription VM SKU restrictions before
provisioning. Paginated usage/SKU readers retain incomplete or denied
reads as non-blocking Unknown. Capacity demand separates immediate
launches from maximum headroom, crediting observed held capacity in the
same family/scope. Explicit or persisted zone restrictions cannot fall
back to another zone; restrictions that do not affect an immediate
launch remain warnings.

Permissions: adds `Microsoft.Compute/locations/usages/read` at
subscription scope alongside the existing SKU catalog read in compute
provision and management sets. It reads applied usage/quota metadata,
without VM inventory or telemetry. No controller-state, Stack or SDK
fields change. Old management roles lacking this permission receive
warnings and continue.

Existing authenticated quota/SKU parser and real usage evidence is
retained in [#1010](#1010).
Regional/family0 and restricted-SKU cases are distinct; this layer makes
no Container Apps managed-environment quota claim. No new cloud
scenarios or resources were created for the split.

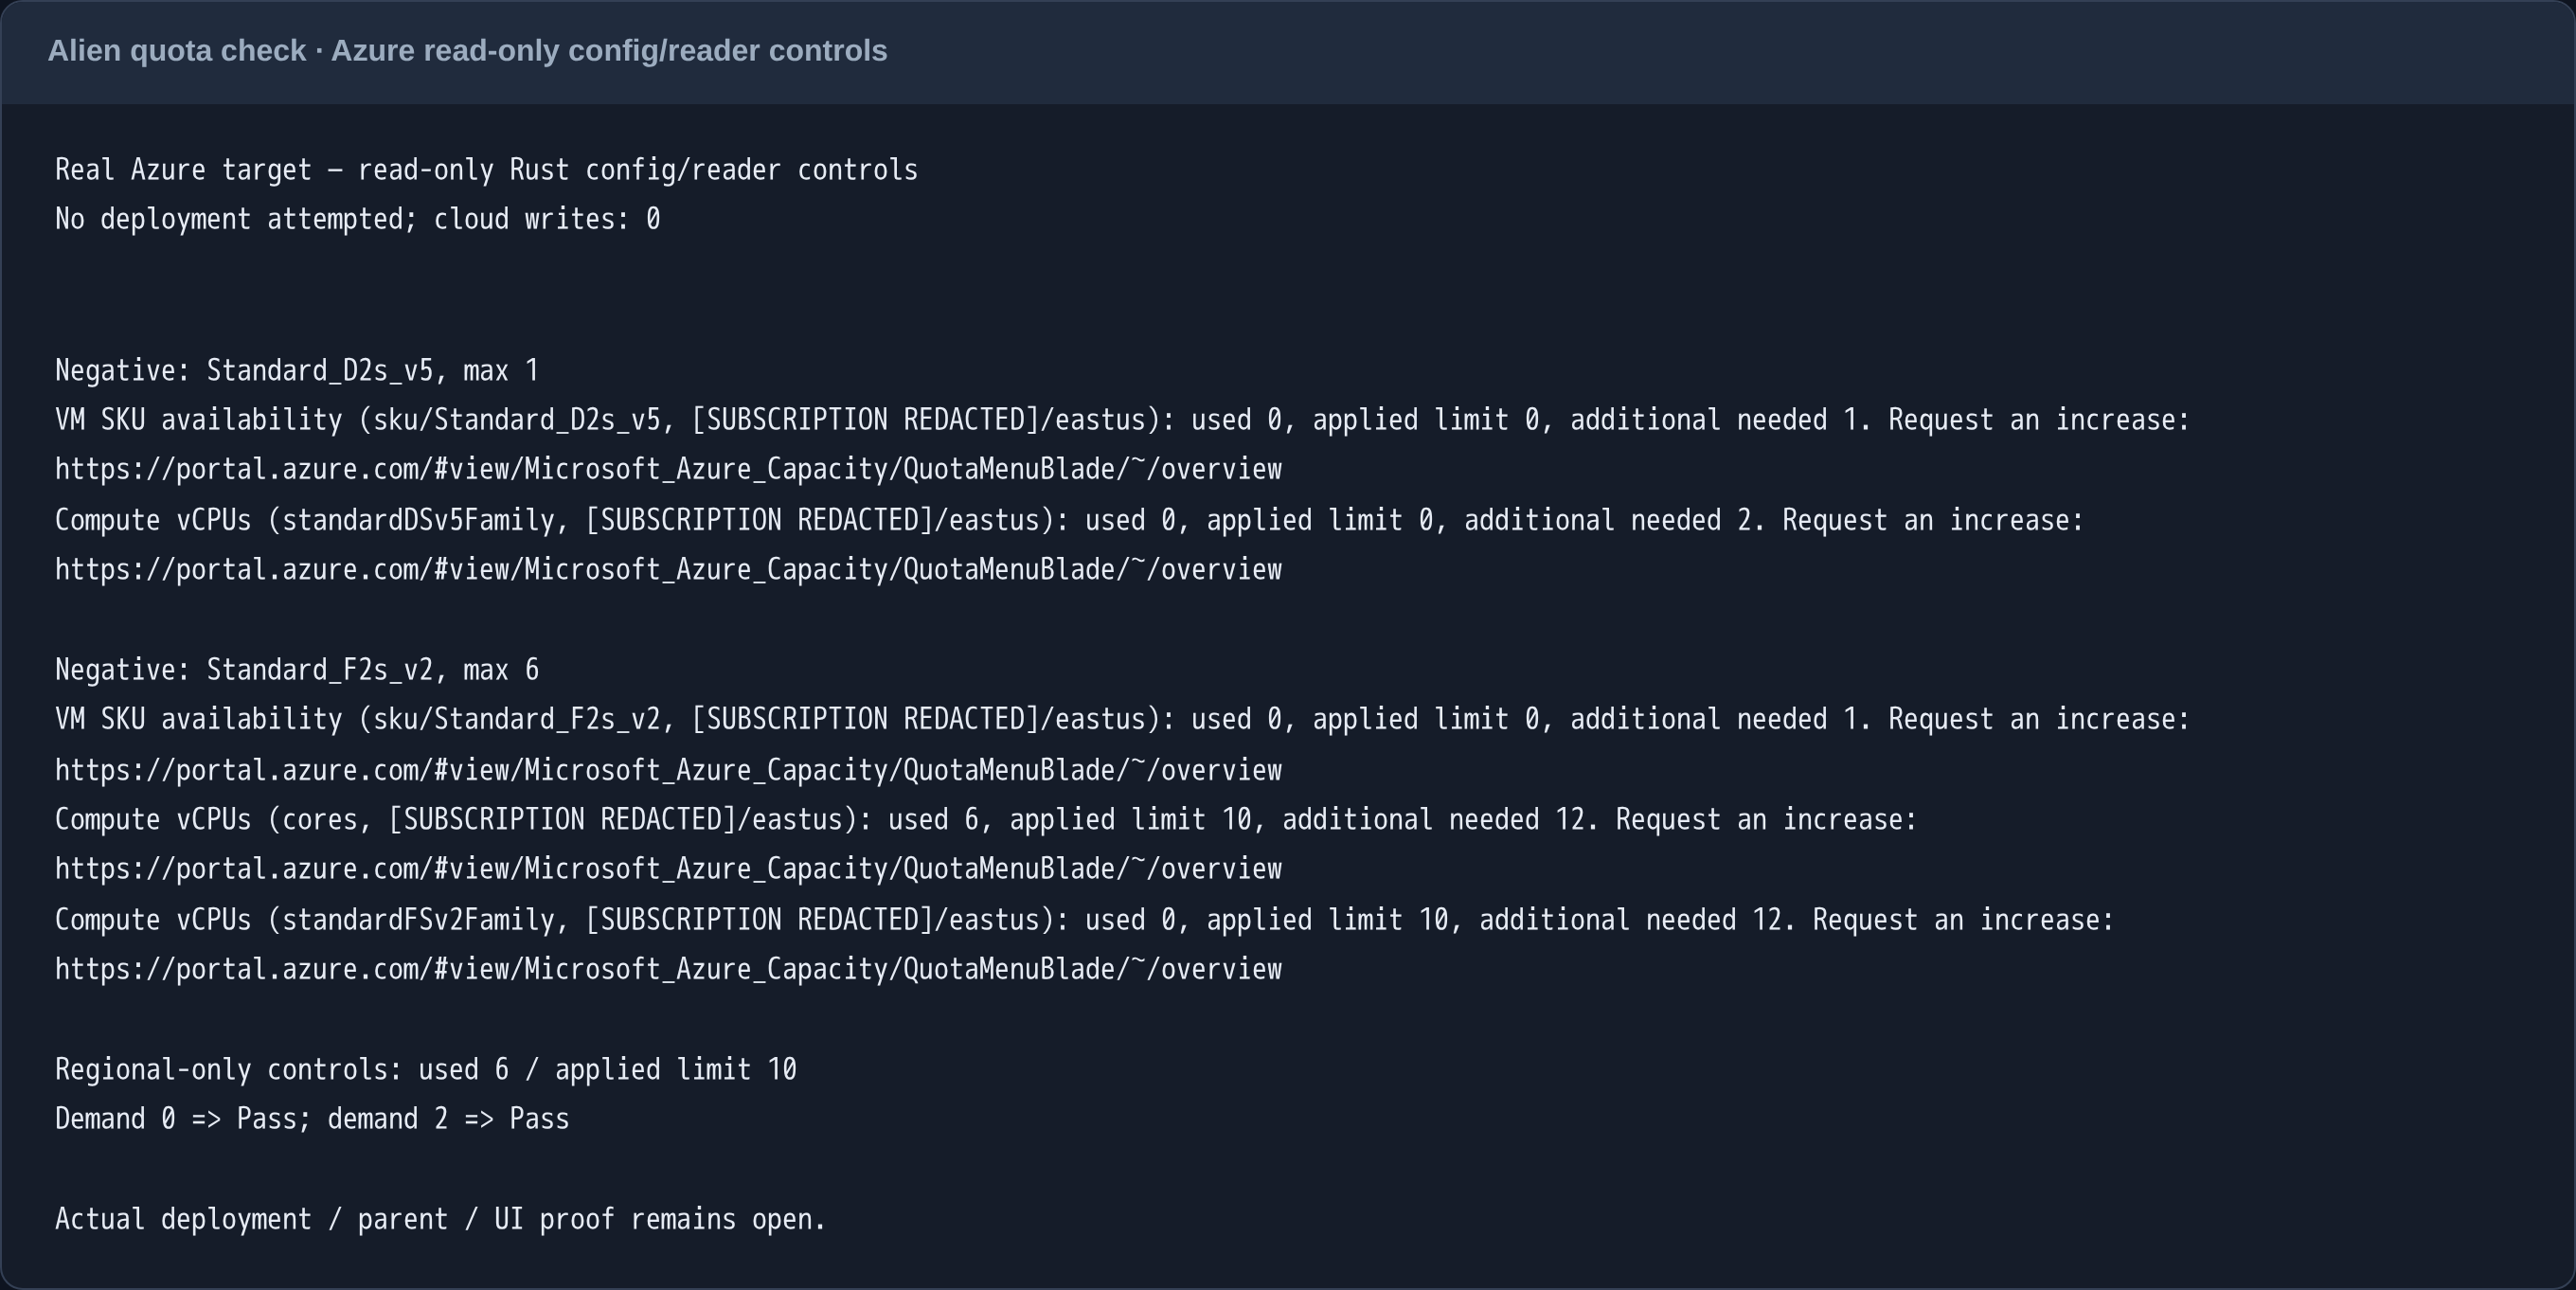
[Existing Azure reader/config
controls](https://raw.githubusercontent.com/alienplatform/alien/pr-assets/alien-5/azure-compute-reader-controls.png)
show regional usage6/applied10 and a family applied0, with simultaneous
SKU/family shortfalls. They performed read-only evaluation and created
no resources.

Compute blocks only when capacity certainly launched by this operation
does not fit. Initial launch uses the configured minimum;
scale-to-maximum shortfalls warn visibly with the quota identity,
shortfall and increase link. Bounds-only changes add no replacement
surge. Instance-type replacement, and effective disk changes on AWS,
count the proven rolling overlap. Late-resolved
image/identity/interrupted-rollout inputs remain a visible Unknown
warning; they never add speculative blocking surge. Observed held
capacity is credited in its original quota pool.

Layer validation: 523 preflight library tests pass, including denied
SKU/usage reads, denied later pages and an independent blocking SKU
restriction. This retains the fix for [Greptile’s missing-read
regression
finding](#1029 (comment)).
Read-only policy control: regional cores6/10, DSv5 family0/0, FSv2
family0/10.

Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer
depends on the preceding PR; human merges only.

Current head `aed360b8c`: **CI green, Greptile 5/5, mergeable and ready
for review**
([review](#1029 (comment))).
The inherited AWS/GCP review fixes are validated; this layer has no
additional source changes.

🤖 Generated with [Claude Code](https://claude.com/claude-code)

Co-authored-by: islo <sandbox@islo.dev>
Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com>
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
1 participant

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Oversized AWS role policies now fail before cloud setup or template output. The build/runtime checks aggregate inline policy characters per role (10,240), bound managed-policy attachments (20), and validate final CloudFormation/Terraform role documents. Shared policy selection/rendering and physical-name helpers keep the calculation aligned with controller writers; incomplete dynamic inputs report their limits explicitly.
Existing before/after evidence:
The native negative parent controls created partial IAM resources; feature rendering rejected with no output files. Positive native setups completed, then normal cleanup removed owned resources. These are existing integrated-feature runs, not reruns on the split commit. Full resolution of every retained/dynamic management policy is not claimed.
No cloud read permissions, protocol/controller-state changes or SDK fields are added by this layer. Pure checks use existing configuration/context; current-stack ownership remains authoritative. Proper supported
pnpm generateand drift checks passed in feature CI38534727697. Independent layer CI and current-head review have passed.Merge order: #1032 → #1026 → #1027 → #1028 → #1029 → #1030. Each layer depends on the preceding PR; human merges only.
The Terraform attachment-reference counting finding remains fixed and covered by the emitted-chunk regression. The latest head inherits the validated AWS/GCP review fixes without additional changes in this layer.
Current head
ec729bbff: CI green, Greptile 5/5, mergeable and ready for review (review).🤖 Generated with Claude Code